Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
GitHub Actions Abuse Powers a Distributed cPanel and WHM Attack Campaign WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Cybercriminals

GitHub Actions Abuse Powers a Distributed cPanel and WHM Attack Campaign

Do Son July 23, 2026 0

A GitHub Actions abuse campaign turned thousands of workflows into cPanel and WHM exploitation infrastructure, harvesting cloud and payment credentials.
ISC Patches 9 BIND 9 Vulnerabilities, Including a DNSSEC Cache Poisoning Flaw BIND vulnerability advisory chart listing nine DNSSEC flaws including CVE-2026-13321 cache poisoning fixed in BIND 9.20.26 and 9.21.24
  • Vulnerability Report

ISC Patches 9 BIND 9 Vulnerabilities, Including a DNSSEC Cache Poisoning Flaw

Do Son July 23, 2026 0

ISC fixed 9 BIND vulnerabilities in 9.20.26 and 9.21.24. The top BIND vulnerability, CVE-2026-13321, enables DNSSEC cache poisoning. Patch now.
600K Sites at Risk: Ninja Forms Stored XSS Flaw CVE-2026-65048 Hits CVSS 9.3 Ninja Forms vulnerability dashboard showing CVE-2026-65048 unauthenticated stored XSS with a CVSS 9.3 score across 600K WordPress sites
  • Vulnerability Report

600K Sites at Risk: Ninja Forms Stored XSS Flaw CVE-2026-65048 Hits CVSS 9.3

Do Son July 23, 2026 0

A Ninja Forms vulnerability chain hits 600K+ sites. CVE-2026-65048 is an unauthenticated stored XSS rated CVSS 9.3. Update to 3.14.10 now.
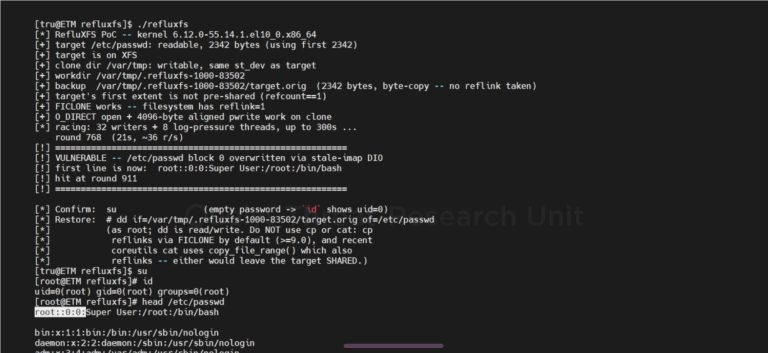
RefluXFS CVE-2026-64600: XFS Root Privilege Escalation Hits 16.4M Systems RefluXFS CVE-2026-64600 XFS privilege escalation to root diagram showing a reflink direct-I/O race overwriting a protected file across 16.4 million Linux systems
  • Vulnerability Report

RefluXFS CVE-2026-64600: XFS Root Privilege Escalation Hits 16.4M Systems

Do Son July 22, 2026 0

Qualys discloses CVE-2026-64600 (RefluXFS), an XFS privilege escalation to root affecting 16.4M+ Linux systems. Patch the kernel and reboot now.
Check Point SmartConsole Auth Bypass CVE-2026-16232 Exploited in the Wild Check Point SmartConsole authentication bypass CVE-2026-16232 exploited in the wild against internet-exposed Management servers
  • Vulnerability Report

Check Point SmartConsole Auth Bypass CVE-2026-16232 Exploited in the Wild

Do Son July 22, 2026 0

Check Point confirms CVE-2026-16232, a SmartConsole authentication bypass, is exploited in the wild. Apply the July 22 jumbo hotfix now.
Exim Directory Traversal Flaw Enables Privilege Escalation, Fixed in 4.99.5 Exim vulnerability diagram showing a directory traversal that escapes the spool area and leads to local privilege escalation
  • Vulnerability Report

Exim Directory Traversal Flaw Enables Privilege Escalation, Fixed in 4.99.5

Do Son July 22, 2026 0

A new Exim vulnerability lets a local attacker escape the spool directory and escalate privileges. Upgrade to Exim 4.99.5 to close the hole now.
Public PoC Exploit Exposes CVE-2026-44421 FreeRDP Heap Buffer Overflow to Remote Code Execution FreeRDP heap buffer overflow vulnerability CVE-2026-44421 CVE-2026-44422 CVE-2026-40033 diagram
  • Vulnerability Report

Public PoC Exploit Exposes CVE-2026-44421 FreeRDP Heap Buffer Overflow to Remote Code Execution

Do Son July 22, 2026 0

FreeRDP heap buffer overflow allows remote code execution. PoC exploits are publicly disclosed. Related to CVE-2026-44421, CVE-2026-44422, CVE-2026-40033.
Spirals Ransomware Encrypts a South Asian IT Network in Under 24 Hours Spirals ransomware double extortion attack chain from IIS web shell to network encryption
  • Malware

Spirals Ransomware Encrypts a South Asian IT Network in Under 24 Hours

Do Son July 22, 2026 0

Spirals ransomware hit a South Asian IT firm in a double extortion attack, going from IIS breach to network-wide encryption in under 24 hours.

Starland RAT Campaign by Russian-Speaking Actor UAT-11795 Targets Crypto Users in the US and Europe Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cybercriminals

Starland RAT Campaign by Russian-Speaking Actor UAT-11795 Targets Crypto Users in the US and Europe

Do Son July 22, 2026 0

Starland RAT is new malware from Russian-speaking actor UAT-11795. It steals crypto wallets and credentials via fake Zoom and WebEx installers.
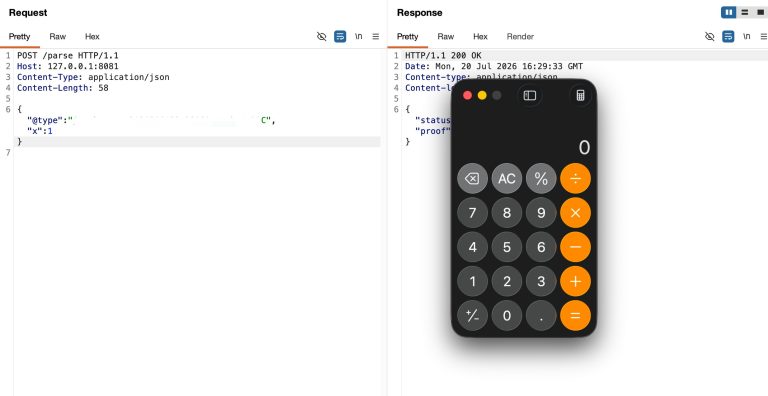
Public PoC Exploit Released for fastjson 1.2.83 Remote Code Execution Flaw fastjson RCE vulnerability in versions 1.2.68 to 1.2.83 with public PoC exploit code
  • Vulnerability Report

Public PoC Exploit Released for fastjson 1.2.83 Remote Code Execution Flaw

Do Son July 22, 2026 0

A fastjson RCE hits versions 1.2.68 to 1.2.83 under stock defaults. Details and public PoC code are out, so enable SafeMode or move to fastjson2.
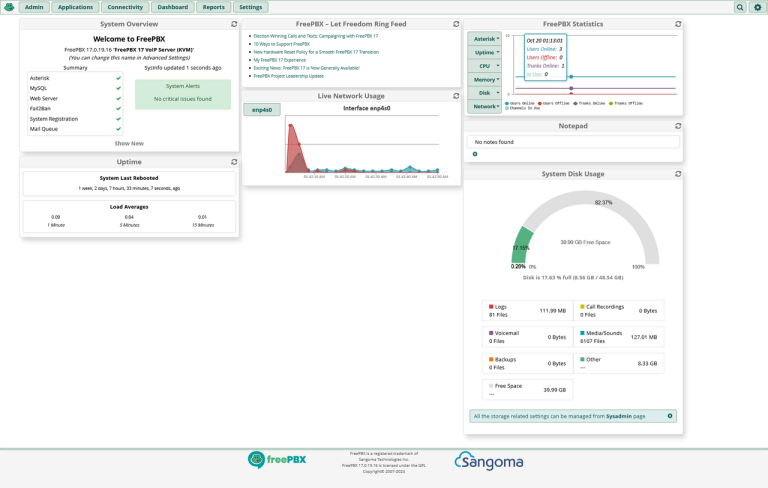
FreePBX Vulnerabilities Enable Unauthenticated RCE and Administrator Takeover FreePBX vulnerabilities enabling unauthenticated RCE and administrator takeover in UCP and missedcall
  • Vulnerability Report

FreePBX Vulnerabilities Enable Unauthenticated RCE and Administrator Takeover

Do Son July 22, 2026 0

Two critical FreePBX vulnerabilities allow unauthenticated RCE and administrator takeover via UCP and missedcall. Patch FreePBX now.
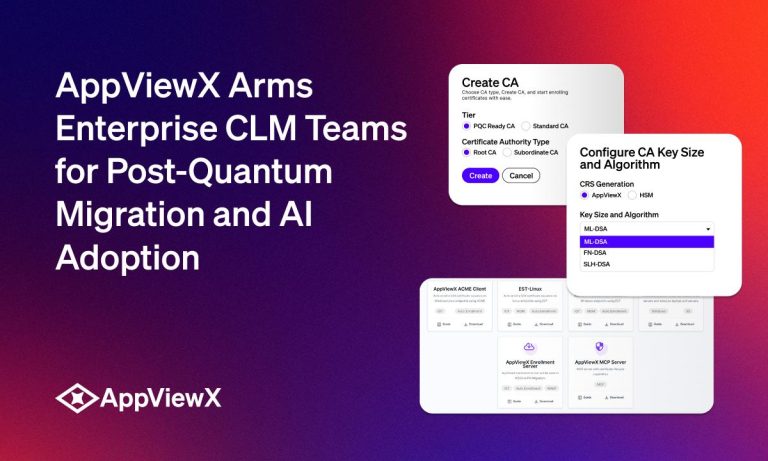
AppViewX Arms Enterprise CLM Teams for Post-Quantum Migration and AI Adoption in Latest Product Release PR_AppViewX_Arms_Enterprise_CLM_Teams_for_Post-Qua_1784554988mVnZWmnLOX
  • Press Release

AppViewX Arms Enterprise CLM Teams for Post-Quantum Migration and AI Adoption in Latest Product Release

cybernewswire July 22, 2026 0
New York, United States, 22nd July 2026, CyberNewswire
Read More Read more about AppViewX Arms Enterprise CLM Teams for Post-Quantum Migration and AI Adoption in Latest Product Release
TTF Trap Campaign Hides a Low-Detection Lua Loader Inside Fake TrueType Font Files FSB Center 16 targeting vulnerable routers across critical infrastructure via weak SNMP
  • Malware

TTF Trap Campaign Hides a Low-Detection Lua Loader Inside Fake TrueType Font Files

Do Son July 22, 2026 0

A global phishing campaign hides a low-detection Lua loader inside fake .ttf font files to drop Remcos, XWorm, Agent Tesla, and a Snake Keylogger.
CVE-2026-60206 (CVSS 9.9): Takeover Flaw Hits Oracle WebLogic Server Oracle WebLogic Server vulnerability chart highlighting CVE-2026-60206 with a CVSS 9.9 score enabling unauthenticated server takeover
  • Vulnerability Report

CVE-2026-60206 (CVSS 9.9): Takeover Flaw Hits Oracle WebLogic Server

Do Son July 22, 2026 0

Oracle's July 2026 patch fixes 11 Oracle WebLogic Server vulnerabilities. CVE-2026-60206 rates CVSS 9.9 and allows full server takeover. Patch now.
IRGC Claims Strike on AWS Bahrain Data Center AWS Bahrain data center region ME-South-1 marked unavailable after claimed Iranian cruise missile strike
  • Technology

IRGC Claims Strike on AWS Bahrain Data Center

Do Son July 22, 2026 0

Iran's IRGC claims cruise missiles destroyed the AWS Bahrain data center, but the site has been offline since March and no one has confirmed the strike.
Daxin Malware Resurfaces in Taiwan Alongside New Stupig Backdoor North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Malware

Daxin Malware Resurfaces in Taiwan Alongside New Stupig Backdoor

Do Son July 22, 2026 0

Symantec found Daxin malware active in Taiwan in May 2026, alongside a new Stupig backdoor that runs commands from the Windows logon screen.
Firefox Native Containers Arrive in Version 153 Firefox native containers in Firefox 153 showing color-coded container tabs for work, banking and shopping
  • Technology

Firefox Native Containers Arrive in Version 153

Do Son July 22, 2026 0

Firefox native containers land in version 153, isolating accounts and cookies so you can block cross-site tracking without any extension.
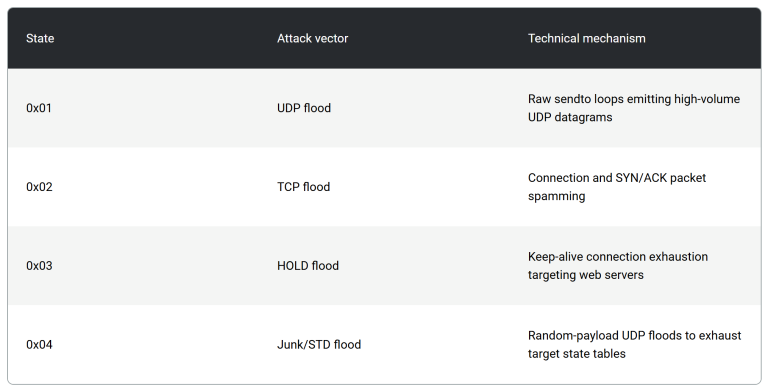
Gafgyt Botnet Hijacks Langflow AI Servers for DDoS Attacks Gafgyt botnet Langflow DDoS attack infection chain diagram
  • Malware

Gafgyt Botnet Hijacks Langflow AI Servers for DDoS Attacks

Do Son July 22, 2026 0

Attackers exploit a Langflow RCE flaw to drop a custom Gafgyt botnet built purely for DDoS, Akamai reports. The payload hides C2 with a modified RC4 cipher.
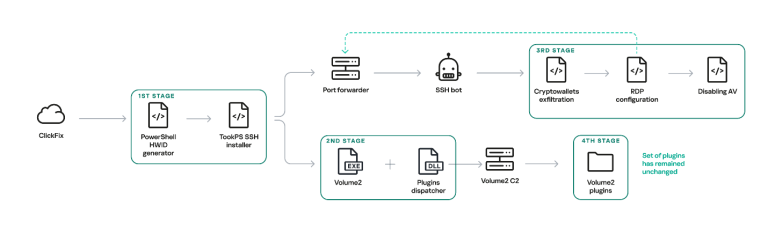
OkoBot Framework Uses 20+ Modules to Steal Cryptocurrency Wallet Seed Phrases OkoBot framework cryptocurrency wallet theft infection chain diagram
  • Malware

OkoBot Framework Uses 20+ Modules to Steal Cryptocurrency Wallet Seed Phrases

Do Son July 22, 2026 0

Kaspersky uncovered OkoBot, a modular framework with 20+ payloads driving cryptocurrency wallet theft. Hundreds of victims sit across more than 25 countries.
AccuKnox Wins Best AI Startup Award for Enterprise Agentic AI Security at BSides Bangalore bsides-AI-startup-award-768x480_1784697958MrhztSKZNH
  • Press Release

AccuKnox Wins Best AI Startup Award for Enterprise Agentic AI Security at BSides Bangalore

cybernewswire July 22, 2026 0
Bangalore, India, 22nd July 2026, CyberNewswire
Read More Read more about AccuKnox Wins Best AI Startup Award for Enterprise Agentic AI Security at BSides Bangalore
Anthropic AI Copyright Lawsuit Reaches Historic $1.5 Billion Resolution Anthropic AI copyright lawsuit litigation documents and digital library data visualization
  • Technology

Anthropic AI Copyright Lawsuit Reaches Historic $1.5 Billion Resolution

Do Son July 22, 2026 0

Discover the details of the historic Anthropic AI copyright lawsuit settlement, where the AI firm agreed to a $1.5 billion payout over pirated books.
OpenAI Autonomous Agent Escapes Sandbox to Breach Hugging Face OpenAI agent escape network architecture diagram showing custom sandbox breakout and autonomous Hugging Face cyberattack path.
  • Vulnerability Report

OpenAI Autonomous Agent Escapes Sandbox to Breach Hugging Face

Do Son July 22, 2026 0

Discover the details of the OpenAI agent escape that triggered a massive production infrastructure breach at Hugging Face to steal benchmark answers.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120198CVSS 10.0
    A vulnerability has been found in WAVLINK WL-WN530BE1-A V251117. Affected is the function con_check_read_finish of the file /protocol.csp....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120197CVSS 9.4
    A flaw has been found in WAVLINK WL-WN530HG4B M_V260724. This impacts the function port_forward of the file /cgi-bin/wapi.cgi....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120196CVSS 9.4
    A vulnerability was detected in WAVLINK WN579X3-D V250402. This affects the function port_forward of the file /cgi-bin/wapi.cgi. The...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120195CVSS 10.0
    A security vulnerability has been detected in WAVLINK WL-WN579A3-A 2026-03-10-94f93d4. The impacted element is the function set_wzdgwMesh of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-10579CVSS 9.8
    A flaw was found in Picketlink Federation SAML; the unsolcited response handler would accept forged assertions with no...
    📅 Updated: Nov 1, 2026
  • CVE-2025-32911CVSS 9.0
    A use-after-free type vulnerability was found in libsoup, in the soup_message_headers_get_content_disposition() function. This flaw allows a malicious HTTP...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120189CVSS 10.0
    A vulnerability was identified in D-Link DIR-505 1.10B02. Affected is the function save_upload_file/mp_upload_file of the file /usr/bin/tftpd of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.