Skip to content
September 28, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Linux
  • Peppermint 9 releases, based on Lubuntu Linux distribution
  • Linux

Peppermint 9 releases, based on Lubuntu Linux distribution

Do Son May 29, 2017 2 minutes read
Peppermint OS
Add Daily CyberSecurity as a preferred source on Google

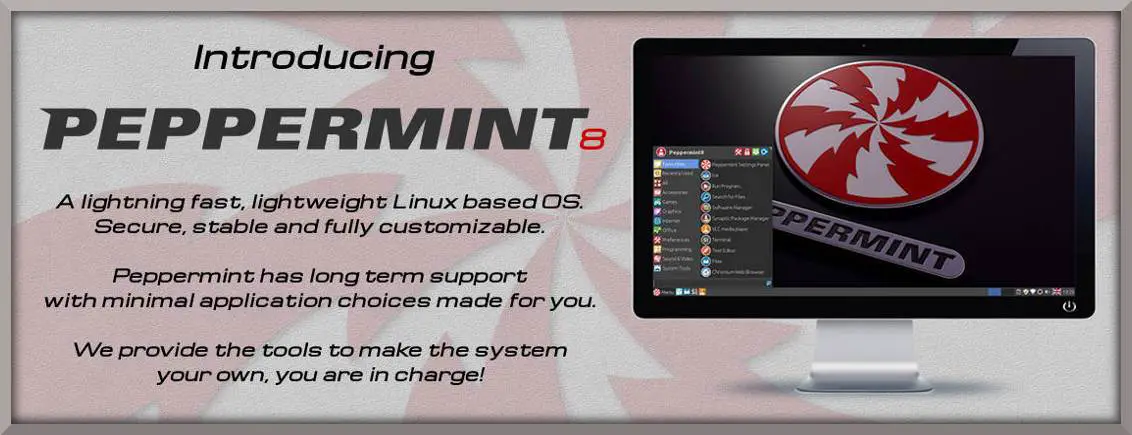
Peppermint OS is based on Lubuntu Linux distribution, its design goal is super fast and low system resource requirements. By using Mozilla’s Prism technology, Peppermint integrates seamlessly with cloud computing and web-based applications. Other features of the release include automatic updates, easy step-by-step installation, elegant and user-friendly interfaces, and enhanced mobility through direct integration with cloud computing applications.

Peppermint announced the availability of the latest version of the Peppermint 8 operating system with 32-bit and 64-bit versions with full UEFI / GPT / Secureboot support, the new version of Ice (internal site-specific browser framework) also includes full Chromium, Chrome, Firefox, and Vivaldi web browsers.

This is a security refresh of the Peppermint 8 ISO images to include all updates to date (as of 3rd Feb 2018), including the Meltdown and Spectre mitigations such as the new HWE kernel 4.13.0-32 and the latest Chromium web browser version 64. The new ISO also contains bug fixes for flash content in ICE SSB’s, and Chromium not remembering user selected xdg-open preferences for magnet and mailto links.

Changelog Peppermint 9

  • We have replaced lxrandr with xfce4-display-setttings for monitor settings as we continue to look for better options that add functionality without adding weight, and to continue the migration away from the few remaining LXDE components.
  • By user request the Menulibre menu editor is now installed by default, and no longer breaks the menus as it did in previous Peppermint versions.
  • Continuing the theme of improved menu and launchere management, there is now a right-click “Create new launcher here” desktop context menu item.
  • The Nemo file manager now has a right-click “Send by email” context menu item. (requires an email client such as Thunderbird to be installed).
  • The Panel Reset function in the Peppermint Settings Panel no longer needs to log you out of your session to reset the panel
  • The Xfce Panel Switch utility is now installed by default, so you can now backup/restore any custom panel configurations and switch between them. It includes a Peppermint-9 default profile and a few others to play with.
  • The system Notification Settings (in the settings panel) now has a “Do Not Disturb” function, or notifications can be enabled/disabled on a per application basis.
  • Qt applications such as VLC now honor the system Gtk theme.
  • Gtk overlay scrollbars are now enabled by default, they’re growing on us 😉
  • More

Download

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Peppermint OS

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-88772
    Memory overflow vulnerability leading to remote code execution or denial of service.
    Admin intelCISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
  • CVE-2026-88771
    Remote code execution due to improper input validation that can allow an unauthenticated attacker to execute arbitrary commands.
    Admin intelCISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
  • CVE-2026-65660CVSS 8.8
    Improper control of generation of code (\'code injection\') in Microsoft Office SharePoint allows an authorized attacker to execute...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 25, 2026
  • CVE-2026-5430CVSS 10.0
    The JWT authentication mechanism accepts tokens signed with algorithms other than those explicitly configured or supported. This allows...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-71362CVSS 9.1
    Adobe Commerce is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    CISA KEV📅 Added to KEV: Sep 24, 2026
  • CVE-2026-48842CVSS 8.1
    Roundcube Webmail 1.6.x before 1.6.16 and 1.7.x before 1.7.1 has Pre-authentication SQL injection in the virtuser_query plugin via...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-87902
    Unauthenticated path traversal in page-template resolution leading to conditional RCE An unauthenticated attacker can make get_page_template() page-template resolution...
    Admin intelCISA KEV📅 Added to KEV: Sep 25, 2026📅 Updated: Sep 23, 2026
  • CVE-2026-94127CVSS 9.8
    When a BIG-IP APM access policy and an OAuth profile is configured on a virtual server, specific malicious...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-100886CVSS 10.0
    A vulnerability was identified in Seetong T8108, T8108P, T8116 and T8232 4.6.1.4-build202604241011. The affected element is an unknown...
    📅 Updated: Sep 27, 2026
  • CVE-2026-88771CVSS 9.5
    Improper input validation vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway. This issue affects ADC: before 14.1-73.37,...
    CISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
  • CVE-2026-88772CVSS 9.5
    Vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway. This issue affects ADC: before 14.1-73.37, before 13.1-64.23, before...
    CISA KEV📅 Added to KEV: Sep 27, 2026📅 Updated: Sep 27, 2026
  • CVE-2026-101090CVSS 9.3
    Nezha 2.2.3 contains a Host header injection regression in the OAuth2 redirect endpoint. When the new optional dashboard_host...
    📅 Updated: Sep 27, 2026
  • CVE-2026-101065CVSS 9.3
    Obot is an open-source AI agent/MCP platform. In all versions up to and including commit d7e6970, the Docker...
    📅 Updated: Sep 27, 2026
  • CVE-2026-101084CVSS 9.3
    obot versions before v0.21.1 fail to enforce Access Control Rules on the /mcp-connect endpoint, allowing any authenticated user...
    📅 Updated: Sep 27, 2026
  • CVE-2026-88773CVSS 9.3
    Inconsistent interpretation of HTTP requests ('HTTP Request/Response smuggling') vulnerability in Citrix NetScaler ADC and Citrix NetScaler Gateway. This...
    📅 Updated: Sep 27, 2026
  • CVE-2026-100741CVSS 9.8
    Eval injection in the JScript event-script dispatcher in Progressive Robot Ltd's hMailServer, versions 6.0.0 through 6.3.3 on Windows,...
    📅 Updated: Sep 27, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.