Skip to content
November 12, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • Technique
  • What is a Port (computer networking)?
  • Technique

What is a Port (computer networking)?

Do Son April 12, 2017 3 minutes read
Pt-port-diagram

What is a Port (computer networking)?

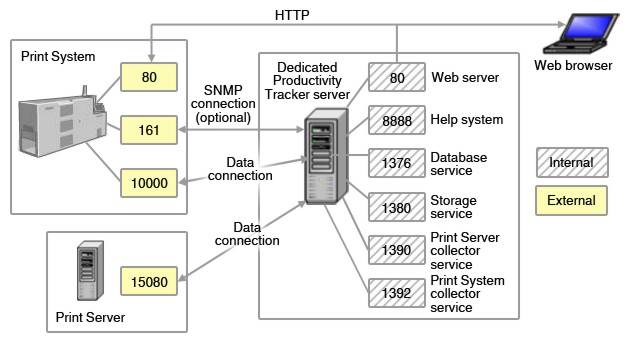
In network technology, the port (Port) generally has two meanings: one is the physical meaning of the port, for example, ADSL Modem, hubs, switches , routers used to connect other network equipment interfaces, such as RJ-45 port, SC port and many more. Second, the logical meaning of the port, generally refers to the TCP / IP protocol port, port number range from 0 to 65535, such as for browsing Web services port 80, 21 ports for FTP services and so on. Ports act as logical commnications endpoints for computers and are used on the Transport layer of the OSI model by protocoal. There are 65536 port altogether, numbering between 0 and 65535.

Port logical sense for a variety of classification criteria, the following describes two common classification:

1. Distribution division by port number

+ Well-known port
Well-known port known as the port number, range from 0 to 1023, these port numbers are generally fixed for some services. For example, port 21 is assigned to the FTP service, port 25 is assigned to the SMTP (Simple Mail Transfer Protocol) service, port 80 is assigned to the HTTP service, port 135 is assigned to the RPC (remote procedure call) service.

+ Registered Ports
Ports used by vendors for proprietary applications, range from 1024-49,151. These must be registered with the IANA. For example, Microsoft registerd 3389 for use with the Remote Desktop Protocol.

+ Dynamic port (Dynamic Ports)
Dynamic port range from 1024 to 65535, these numbers are generally not assigned to a fixed service, that many services can use these ports. Just run the program to the system application to access the network, the system can be allocated from a number of these ports for the program. For example, 1024 port is assigned to the first system to apply for the program. After closing the program process, it will release the occupied port number.

However, the dynamic port is also often used by the virus Trojans, such as the glacial default connection port is 7626.

2. Classification by protocol

by protocol type division, can be divided into TCP, UDP, IP and ICMP (Internet Control Message Protocol) port. The following describes the TCP and UDP port:

+ TCP port

TCP port that Transmission Control Protocol ports required to establish a connection between the client and the server, which can provide reliable data transmission. Commonly, FTP port 21, Telnet 23, SMTP 25, HTTP 80, and so on.

+ UDP port

UDP port that the user datagram protocol port, without the need to establish a connection, security can not be guaranteed between the client and the server. Common DNS services are 53 ports.

Tags: Port (computer networking)

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-90908CVSS 9.3
    A vulnerability in the GenericAdminAuthenticator component of Azul Payara Server and Azul Payara Micro allows a remote, unauthenticated...
    📅 Updated: Nov 12, 2026
  • CVE-2026-110003CVSS 9.3
    A vulnerability in the administration REST interface of Azul Payara allows a remote, unauthenticated attacker to bypass secure-admin...
    📅 Updated: Nov 12, 2026
  • CVE-2026-8333CVSS 9.4
    A stored cross-site scripting vulnerability in Microchip the TimePictra platform could allow an authenticated, low-privileged attacker to store...
    📅 Updated: Nov 12, 2026
  • CVE-2026-12591CVSS 9.9
    Zohocorp ManageEngine M365 Manager Plus versions below 4818 is affected by an authenticated technician may exploit insufficient permission validation in the delegated administration...
    📅 Updated: Nov 12, 2026
  • CVE-2026-12507CVSS 9.1
    Zohocorp ManageEngine AssetExplorer versions below 7860, ServiceDesk Plus versions below 15290, ServiceDesk Plus MSP versions below 15150, and...
    📅 Updated: Nov 12, 2026
  • CVE-2026-107935CVSS 9.3
    A path traversal vulnerability was found in gvproxy, the network forwarder provided by the gvisor-tap-vsock package. The unauthenticated...
    📅 Updated: Nov 12, 2026
  • CVE-2026-125883CVSS 9.3
    Improper restriction of XML external entity reference vulnerability in N-able N-central allows XML Schema Poisoning. This issue affects...
    📅 Updated: Nov 12, 2026
  • CVE-2026-76954CVSS 9.8
    An improper neutralization of special elements used in an SQL command vulnerability in the Auth API in Synology...
    📅 Updated: Nov 12, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.