Skip to content
November 12, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • Technique
  • Protect yourself from cyberstalkers
  • Technique

Protect yourself from cyberstalkers

Do Son December 12, 2019 4 minutes read
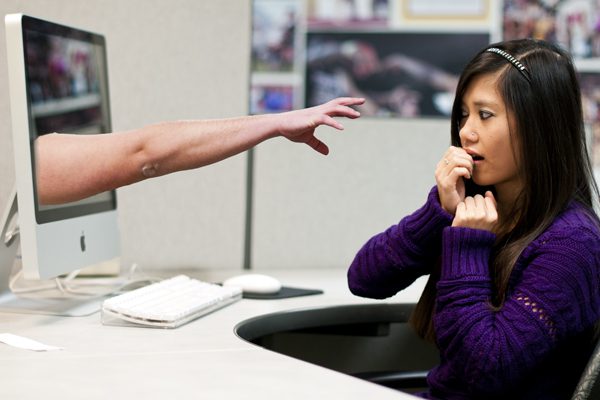
protect cyberstalkers

The internet has brought us all closer together than ever before. Never before in our history has mankind been able to communicate so seamlessly. However, in the darker realms of the internet, such freedom is often misused for nefarious purposes.

Cyberstalking is defined as being stalking or harassment towards an individual that is carried out over the internet. Cyberstalking comes in several different forms that range from slander and unwanted messages to death threats and actual physical violence.

Prior to the introduction of social media, harassment was much more difficult due to the lack of obtainable information on a particular person. Nowadays, however, people freely share sensitive information and post pictures of themselves and their families. Hence this makes it much easier for a creep to gather information on their victims or even track them down.

Oftentimes, victims are usually unaware that they’re victims of cyberstalking. Social media such as Facebook and Instagram have made it extremely easy for a stalker to monitor his/her victim from afar without being noticed. Pseudo-celebrities or influencers often welcome such unwanted attention and at times, negative comments or innuendos are in fact used by them to gain further traction.

However, when unwanted or threatening comments are regularly received, then the victim should be aware that a line has been crossed. Perpetrators of cyberstalking tend to be driven by a variety of reasons with the most common being jealousy, revenge, and lust.

With all of that in mind, here’s our guide to how you can protect yourself from becoming a victim of cyberstalking:

  1. Maintain a low-profile online

The internet exposes us to all kinds of people from all over the world. While most of them are decent folk, a small percentage is up to no good. Hence, it’s often best to keep as low a profile as you can while online.

Avoid sharing information related to your place of employment, hometown, and family. Hackers and stalkers have been known to collect such information in order to make use of it to intimidate or harass their victims. Obviously avoid revealing information such as phone numbers and addresses at all costs.

While we believe in flaunting it if you have it, social media is not really the type of place to share “sensitive” images of yourself or your SO. You’ll never know who could get their hands on such information. As we’ve seen from the 2014 iCloud breach, you’ll never know what may end up on the internet and used against you.

  1. Keep your software updated

While app and software updates can be bothersome at times, they are extremely critical. Oftentimes they contain important patches that deal with potential security breaches.

Thus, whenever you have an update available, take the extra time to make sure that you get everything updated. After all, it only takes a few minutes and ensures that your privacy remains protected.

  1. Sanitize yourself

Social media has provided us with a platform to share aspects of our lives with friends and family. However, more often than not folks tend to take things to the extreme and turn Facebook into a political battleground.

Often, you can tell a lot about a person based on what he/she shares on social media. While you may be tempted to add your say, sometimes it’s just better to take the high road. Forget getting into any arguments and leave things as they are.

Posting inflammatory posts that touch on race, religion or politics can be used to hurt you later on by someone who may not agree with you.

If you find yourself being stalked or harassed online, don’t hesitate to block the person and report them to the relevant moderators. Should the harassment escalate faster than a Kentucky Derby horse race, make a police report and take a break off social media? Removing your virtual presence makes it that much more difficult for a stalker to track you down.

Tags: protect cyberstalkers

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123039CVSS 7.8
    The Gaia OS DynamicCLI daemon runs as root and listens on a world-writable local socket (/tmp/dynamic_socket) without authenticating...
    Admin intel📅 Updated: Nov 12, 2026
  • CVE-2026-20320CVSS 7.5
    A vulnerability in the Open Client Interface (OCI) XML Parser of Cisco BroadWorks could allow an unauthenticated, remote...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-111560CVSS 8.6
    Improper neutralization of shell metacharacters in the timezone configuration field in certain Barracuda appliance products using common Barracuda...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-116606CVSS 9.3
    An authentication bypass in Barracuda Email Security Gateway versions earlier than 9.4.0.030 allows an unauthenticated remote attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-124194CVSS 6.5
    Product ui does not warn user of unsafe actions in Microsoft Office Outlook allows an unauthorized attacker to...
    CISA KEV📅 Added to KEV: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-17131CVSS 9.3
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to obtain sensitive information due to server-side...
    📅 Updated: Nov 12, 2026
  • CVE-2026-17344CVSS 9.3
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to obtain sensitive information due to server-side...
    📅 Updated: Nov 12, 2026
  • CVE-2026-63857CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: net: airoha: Do not read uninitialized fragment address...
    📅 Updated: Nov 12, 2026
  • CVE-2026-121355CVSS 9.1
    Adobe Connect is affected by an Incorrect Authorization vulnerability that could result in privilege escalation. An attacker could...
    📅 Updated: Nov 12, 2026
  • CVE-2026-120869CVSS 9.4
    An unauthenticated attacker can bypass authentication controls to access restricted resources on the appliance Pre-conditions: Access to Citrix...
    📅 Updated: Nov 12, 2026
  • CVE-2026-120864CVSS 9.3
    Memory overflow in ICA proxy can lead to unpredictable or erroneous behavior or Denial of Service. Pre-conditions: The...
    📅 Updated: Nov 12, 2026
  • CVE-2026-107412CVSS 9.5
    Multiple Memory overflow vulnerabilities can lead to unpredictable or erroneous behavior and Denial of Service Pre-conditions: NetScaler is...
    📅 Updated: Nov 12, 2026
  • CVE-2026-107415CVSS 9.3
    Memory overflow in Email OTP authentication can lead to unpredictable or erroneous behavior or Denial of Service. Pre-conditions:...
    📅 Updated: Nov 12, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.