Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • Linux
  • Smoothwall Express 3.1 released, best-of-breed Internet firewall/router
  • Linux

Smoothwall Express 3.1 released, best-of-breed Internet firewall/router

Do Son April 26, 2018 3 minutes read
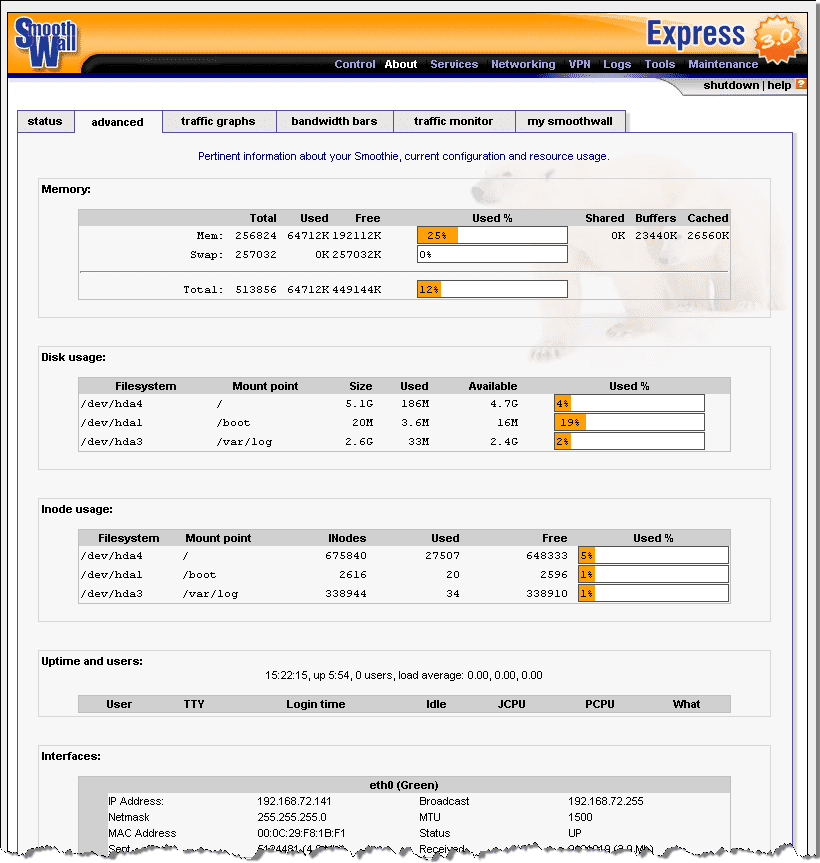
Smoothwall

The Smoothwall Open Source Project was set up in 2000 to develop and maintain Smoothwall Express – a Free firewall that includes its own security-hardened GNU/Linux operating system and an easy-to-use web interface.

The Smoothwall GPL project was founded in the summer of 2000 by Lawrence Manning (Principle Code Author) and Richard Morrell (Project Manager). Their goal was to create a Linux distribution that could convert a redundant PC into a hardened internet firewall device. With help from other early contributors; Jon Fautley and Tom Ellis, the first Smoothwall Firewall was posted to sourceforge.net at the end of August 2000.

The project was immediately popular and grew rapidly. Within weeks, thousands of copies had been downloaded and Smoothwall was appearing regularly on magazine cover CDs in the UK and overseas. Many more developers joined the team and new versions were released almost weekly, incorporating new features based on software contributions from all around the world.

Over the years, the project team has changed and the Smoothwall community has grown to include almost 17,000 forum members.
The goals of the project can be summed up as:

  • Be simple enough to be installed by home users with no knowledge of Linux
  • Support a wide variety of network cards, modems, and other hardware
  • Work with many different connection methods and ISPs from across the world
  • Manage and configure the software using a web browser
  • Run efficiently on older, cheaper hardware
  • Develop a supportive user community
  • Use sponsorship from Smoothwall Limited to further these goals

Smoothwall Express 3.1 released.

Changelog:

  • The build system is vastly improved. It is now re-entrant (a build will continue where it left off when an error is encountered and fixed), and compiles will use all CPU cores present). It should produce correct i586 or x86_64 code for all packages.
  • Grub Legacy is now used to boot all drives: ISO images, flash installers, and the installed target.
  • SMP is standard for 32- and 64-bit installations. Smoothwall Express will now use those extra CPU cores.
  • Installation on KVM, Xen, VMWare, Hyper-V and other virtual systems is supported. Operation on KVM was used extensively during development; operation on other hypervisor systems is known to work but hasn’t been tested as thoroughly. Virtio disk and network devices are supported; they work well with KVM.
  • The kernel now provides /dev entries for all devices it knows about; udev handles the rest.
  • The latest firmware blob from kernel.org has been included to make more hardware usable with Smoothwall Express.
  • The collection of manufacturer drivers for NICs and NADs has been moved into a separate package to make it easier to provide updates.
  • More…

Download

Add Daily CyberSecurity as a preferred source on Google

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Smoothwall

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-49121CVSS 9.2
    AI Tensor Engine for ROCm (AITER) through 0.1.14 contains an unauthenticated remote code execution vulnerability in the MessageQueue.recv()...
    📅 Updated: Nov 8, 2026
  • CVE-2026-48242CVSS 9.2
    Open ISES Tickets before 3.44.2 contains hardcoded MySQL database connection credentials (host, username, password, database name) in import_mdb.php....
    📅 Updated: Nov 8, 2026
  • CVE-2026-48241CVSS 9.2
    Open ISES Tickets before 3.44.2 contains hardcoded MySQL database credentials in loader.php (a public-facing database utility) that are...
    📅 Updated: Nov 8, 2026
  • CVE-2026-47117CVSS 9.3
    OpenMed before 1.5.2 contains a remote code execution vulnerability in the PII privacy-filter model loading path. The privacy-filter...
    📅 Updated: Nov 8, 2026
  • CVE-2026-47103CVSS 9.3
    Python StateMachine versions 3.0.0 before 3.2.0 contains a remote code execution vulnerability that allows attackers to execute arbitrary...
    📅 Updated: Nov 8, 2026
  • CVE-2026-43633CVSS 9.5
    HestiaCP versions 1.9.0 through 1.9.4 contain a deserialization vulnerability in the web terminal component caused by a session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-42796CVSS 9.2
    Arelle before 2.39.10 contains an unauthenticated remote code execution vulnerability in the /rest/configure REST endpoint that accepts a...
    📅 Updated: Nov 8, 2026
  • CVE-2026-41947CVSS 9.3
    Dify before version 1.14.2 contains an authorization bypass vulnerability that allows authenticated editor users to set and enable...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.