Skip to content
October 21, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • Technique
  • SSH port forwarding
  • Technique

SSH port forwarding

Do Son April 30, 2017 5 minutes read
1

SSH automatically encrypts and decrypts the network data between all SSH clients and the server. This process is sometimes called “tunneling” (tunneling), because SSH for other TCP links to provide a secure channel for transmission and named. For example, Telnet, SMTP, LDAP these TCP applications can benefit from, to avoid the user name, password and privacy information in clear text transmission. At the same time, if the firewall in your work environment limits the use of some network ports, but allows SSH connections, then you can also forward the TCP port to use SSH to communicate.

SSH port forwarding can forward the network data of other TCP ports through SSH link, and automatically provide the corresponding encryption and decryption services.

There are four ways, namely, local forwarding, remote forwarding, dynamic forwarding, X protocol forwarding.

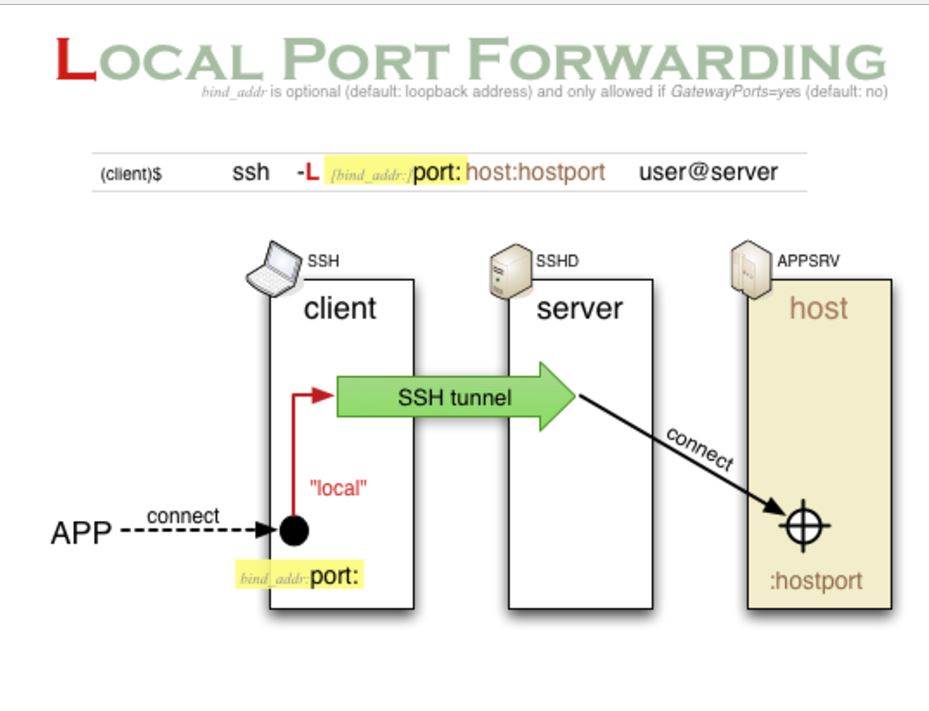
  1. Local Port Forwarding
    SSH connection and application connection The two connections are in the same direction. Localhost parameters can be omitted. The default is 0: 0: 0: 0, but for security reasons, it is necessary to set the localhost parameter. ssh -L [<local host>:]<local port>:<remote host>:<remote port> <SSH hostname> Use 127.0.0.1 as the local listening port.One port of the local machine (client) is forwarded to the designated port of the remote designated machine; the local port forwarding is listening on a port on the localhost, and all the data accessing the port is transmitted to the remote port through ssh tunnel.

    as follows:

    localhost: ssh -L 7001:localhost:7070 sisca@216.194.70.6

    Before landing Localhost port Monitoring status:

     
    After landing the localhost port listening status:
     After the remote host will not listen to the port. Summary: local port forwarding time, the local ssh monitor 7001 port.
  2. Remote Port Forwarding
    SSH connection and application connection The two connections are in the opposite directions -R [<local host>:]<local port>:<remote host>:<remote port> <SSH hostname>, localhost parameters can be omitted, the default is 0:0:0:0, for security must use 127.0 .0.1 as a local listening port.One port of the remote host (server) is forwarded to the designated port of the designated machine on the local side; the remote port forwarding is listening on one port on the remote host. All the data of the designated port of the remote server is transmitted to the local counterpart through the ssh tunnel port.
    as follows:
    localhost: ssh -R 7001:localhost:7070 sisca@216.194.70.6
    Before landing Localhost port Monitoring status:

    After landing the localhost port listening status:
    Remote host port after listening Status:
    Summary: the use of remote port forwarding, the localhost port monitoring and did not change, on the contrary, the remote host began to listen to our designated 7001 port.
  3. Dynamic Port Forwarding
    The remote ssh server as a secure proxy server ssh -D [<local host>:]<local port> <SSH hostname>, localhost parameters can be omitted, the default is 0:0:0:0, for security, must use 127.0.0.1 as a local listening port.The establishment of a dynamic SOCKS4 /5 proxy channel, followed by the local monitoring of the port number; dynamic port forwarding is to establish an ssh encrypted SOCKS4/5 proxy channel, any support SOCKS4/5 protocol procedures can use this encrypted Channel to the agent to visit, and now the most commonly used method is to over the wall.

    as follows:
    localhost: ssh -D 7070 sisca@216.194.70.6

    Before landing Localhost port Monitoring status:

    After landing the localhost port listening status:
    Summary: When using dynamic port forwarding, the local host’s ssh process is listening on the specified 7070 port.
  4. X Protocol Forwarding
    The remote ssh server as a secure proxy server.
    ssh -X  <SSH hostname>
    For example, we may often log on to Linux/Unix/Solaris/HP and other machines to do some development or maintenance, and often need to run some GUI programs, such as the graphical interface to install DB2/WebSphere and so on. This time there are usually two options to achieve: VNC or X window, let us look at the latter. A more common scenario is that our local machine is the Windows operating system, then you can choose to open source XMing as our XServer, and SSH Client can be arbitrarily selected, such as PuTTY, Cygwin can be configured to visit SSH at the same time to establish X forward.

    SSH port forwarding In addition to the above four representatives of the different working parameters of the parameters, there are some ancillary parameters:-C: compressed data transmission-N: Do not execute scripts or commands, usually associated with -f

    -f: background authentication user/password, usually used in conjunction with -N, do not have to log on to the remote host, if through other procedures to control the tunnel connection, should avoid the SSH client into the background, that is, remove the-f parameter.

    -g: In the -L / -D / -R parameter, the remote host is allowed to connect to the established forwarding port. If this parameter is not added, only the local host is allowed to establish a connection.

Tags: ssh Dynamic Port Forwarding ssh Local Port Forwarding ssh Remote Port Forwarding ssh X Protocol Forwarding

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 21, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 21, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 21, 2026
  • CVE-2012-20002CVSS 8.7
    TinyMCE Thumbnail Gallery plugin for WordPress before 1.1.0 contains a path traversal vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Oct 21, 2026
  • CVE-2012-20003CVSS 5.1
    Custom Tables plugin for WordPress before 3.4.6 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Oct 21, 2026
  • CVE-2012-20004CVSS 5.1
    K-news plugin for WordPress before 1.1.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject...
    Watchtower Verified📅 Updated: Oct 21, 2026
  • CVE-2026-66373CVSS 7.5
    Redis before 8.8.0, in the unusual case where an authenticated attacker can execute RESTORE, allows remote code execution...
    Admin intel📅 Updated: Oct 20, 2026
  • CVE-2026-96652CVSS 5.3
    Plex Media Server before 1.43.3.10861 allows SSRF via '/player/timeline'. An attacker using any X-Plex-Token value can include a...
    CISA KEV📅 Added to KEV: Oct 20, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-71195CVSS 9.9
    In OpenStack Manila before 23.0.1, multiple Manila API operations on public shares do not verify that the caller...
    📅 Updated: Oct 21, 2026
  • CVE-2026-106173CVSS 9.8
    A improper limitation of a pathname to a restricted directory ('path traversal') vulnerability in Fortinet FortiSIEM 7.5.0 may...
    📅 Updated: Oct 21, 2026
  • CVE-2026-86471CVSS 9.3
    An unvalidated runtime configuration value in Apache CouchDB 3.5.2 and below on all platforms allows a CouchDB server...
    📅 Updated: Oct 21, 2026
  • CVE-2026-26846CVSS 9.8
    Buffer Overflow vulnerability in WEINVEIW CO.,LTD EBPro v.6.10.01.510_20251022 allows a remote attacker to execute arbitrary code via the...
    📅 Updated: Oct 21, 2026
  • CVE-2026-111281CVSS 9.3
    Jooan JA-A12 IP cameras with firmware 009_20171107 and 05.02.31.105 contain a remote code execution vulnerability that allows unauthenticated...
    📅 Updated: Oct 21, 2026
  • CVE-2026-113744CVSS 10.0
    A security vulnerability has been detected in Tenda AC19 16.03.10.07. The impacted element is the function formSetFirewallCfg of...
    📅 Updated: Oct 21, 2026
  • CVE-2026-57496CVSS 9.6
    NetLicensing MCP Server is a natural-language interface that enables agentic applications to manage the software-licensing lifecycle in Labs64...
    📅 Updated: Oct 21, 2026
  • CVE-2026-113342CVSS 9.6
    Memory corruption in Network in Google Chrome prior to 156.0.8078.47 allowed a remote attacker to execute arbitrary code...
    📅 Updated: Oct 21, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.