
 Do Son
Scammers are leveraging Amazon SES and leaked IAM keys to bypass security filters. Learn how to protect your organization from this high-trust phishing surge.
Amazon SES
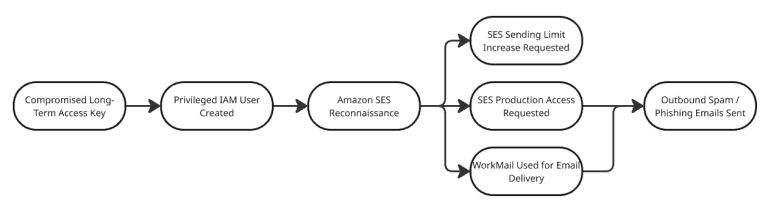
Attackers are bypassing AWS SES sandbox limits by pivoting to WorkMail. Rapid7 reveals how this abuse creates a blind spot for defenders.

A new report reveals how a compromised AWS key was used to bypass security controls in Amazon SES, enabling a 50,000-email-per-day phishing campaign.