 Do Son
A macOS ClickFix campaign now uses a browser fingerprinting gate to hide AMOS infostealer lures from researchers. See how it works.
AMOS
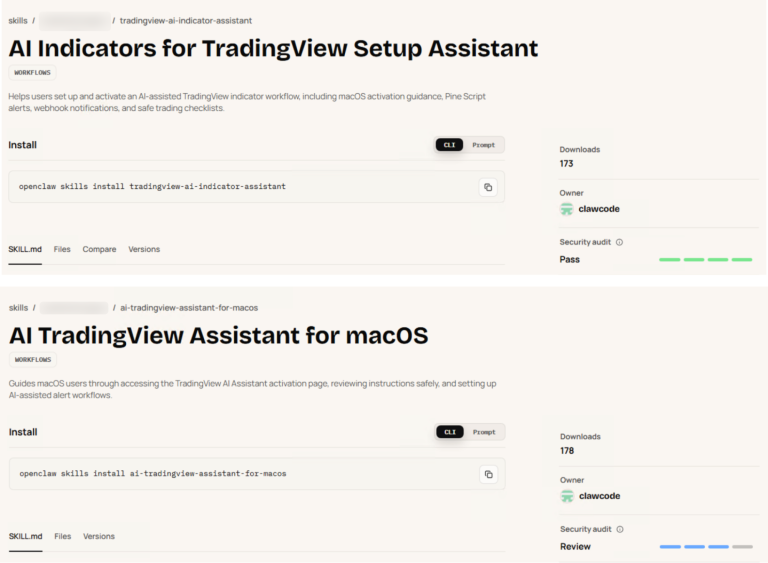
Unit 42 found five malicious OpenClaw skills on ClawHub that bypassed scanners. The AI supply chain attack delivered infostealers and crypto fraud.
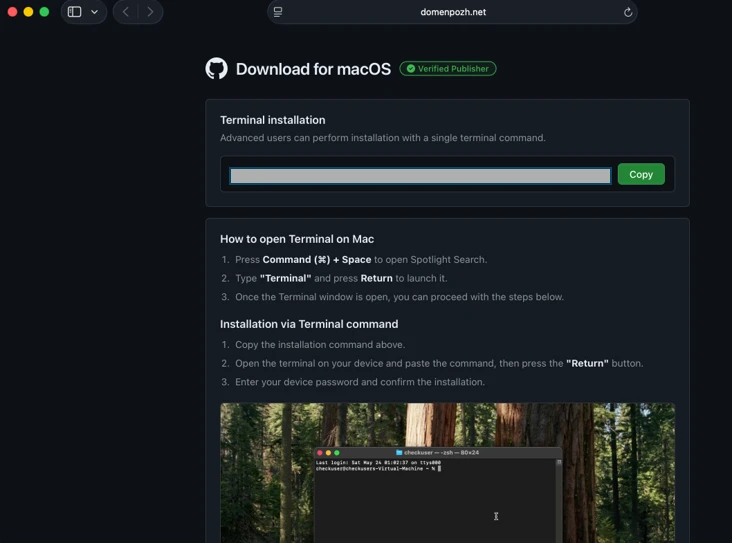
Microsoft reveals a macOS ClickFix campaign using fake "fixes" to trick users into running Terminal commands that bypass Gatekeeper and steal crypto wallets.

Microsoft warns: Infostealers now target macOS & use WhatsApp worms. "Eternidade" & "Crystal PDF" steal credentials via cross-platform attacks.

VirusTotal warns of massive supply chain attack on OpenClaw. Hackers use fake "skills" to deploy malware like Atomic Stealer. Verify your agents.

A new report reveals the AMOS infostealer is targeting macOS. The malware is spread via fake apps and malicious Terminal commands that bypass Gatekeeper.

AMOS malware just leveled up—now a backdoor, it poses a serious threat to macOS with persistent access and remote command execution.

A new macOS information stealer, a potential AMOS variant, targets crypto users and Ledger Live accounts, stealing passwords and wallet data using stealthy daemonization and local admin prompt tactics.

A new AMOS macOS stealer variant is using typo-squatted Spectrum domains in a clever cross-platform social engineering campaign. Stay vigilant!

Uncover the operations of the prolific cybercriminal group Crazy Evil. Dive into their sophisticated social engineering tactics and cross-platform malware toolkit.

Mac users are facing renewed challenges from an insidious form of malware known as the Atomic Stealer, or AMOS

The ingenuity of malware distribution is exemplified by the FakeSG campaign, a sinister operation that employs a NetSupport RAT