 Do Son
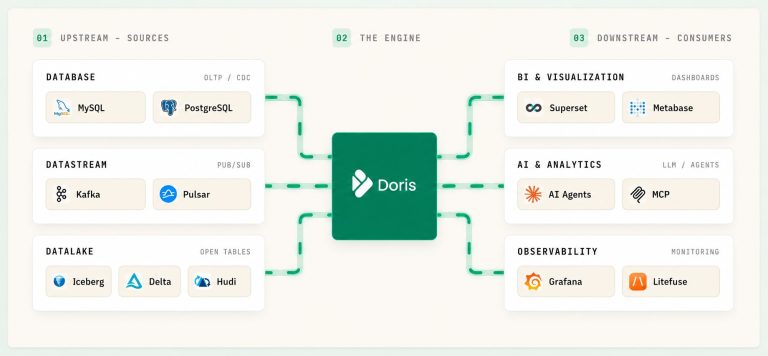
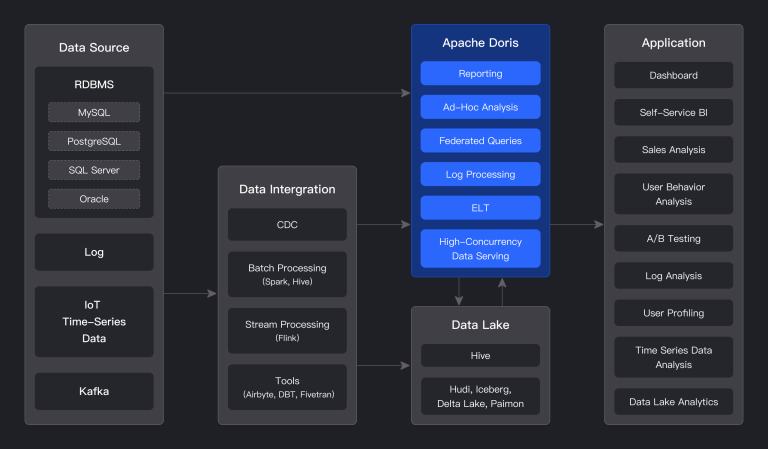
The team patched Apache Doris vulnerabilities in new updates. Learn how these Apache Doris vulnerabilities impact clusters and update now.
Apache Doris
Apache Doris vulnerability CVE-2026-58319 lets unauthenticated attackers hit FE HTTP admin APIs. Upgrade to Doris 3.1.0 now to close the flaw.
A critical Apache Doris SQL injection vulnerability identified as CVE-2025-66336 allows attackers to bypass authentication. Upgrade your servers now.

Given the severity of CVE-2024-27438, Apache Doris users are strongly advised to upgrade to version 2.0.5 or 2.1.x immediately

CVE-2023-41313 allows attackers to exploit weaknesses in the authentication process within Apache Doris using a timing attack