 Do Son
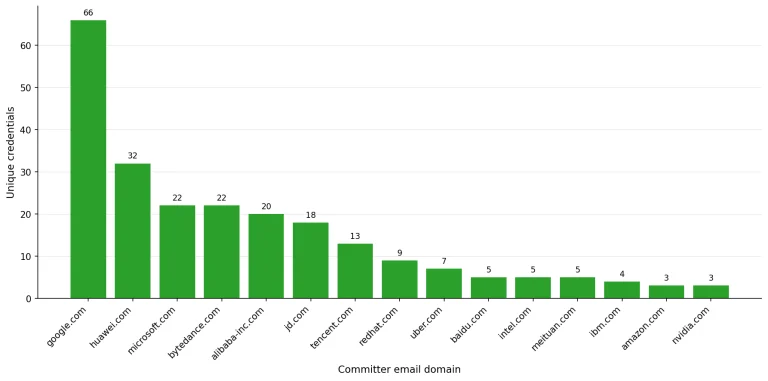
A security scan revealed over 26,000 Gitee exposed credentials across 7.25 million public repositories, affecting major cloud and AI platforms.
API keys
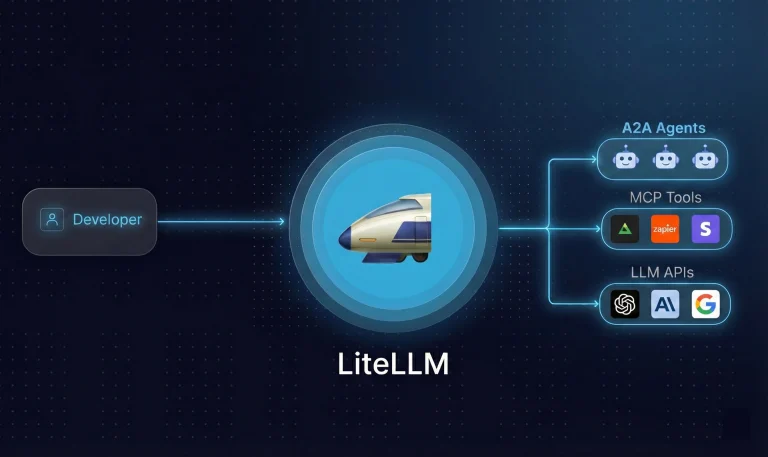
A critical LiteLLM vulnerability (CVSS 10.0) lets an unauthenticated file read leak the master key on Enterprise proxies. Update to 1.106.5 now.
The Zeabur platform shutdown is set for December 2026 after an attacker read 3.21 million environment variables and 321,800 accounts.
Railway security incident: attackers may have decrypted Railway environment variables. Builds are paused. Rotate API keys and credentials now.
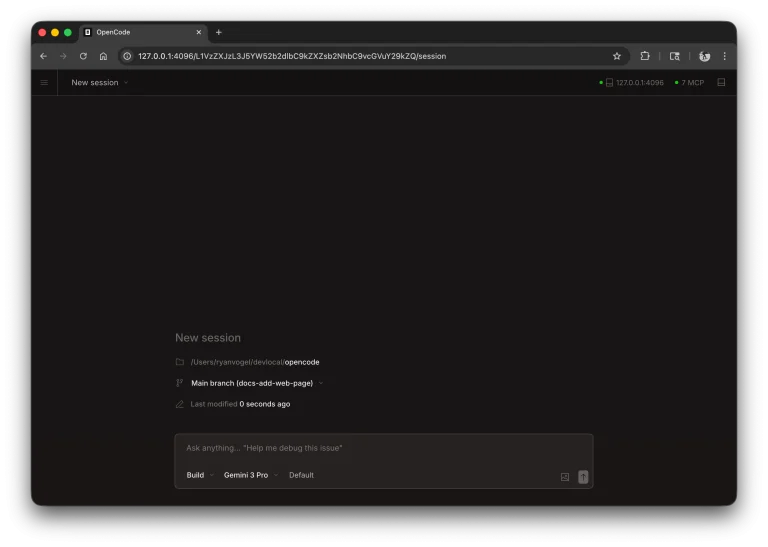
The OpenCode security breach may have exposed stored third-party API keys for 1.4% of Console users. Revoke and rotate keys now.
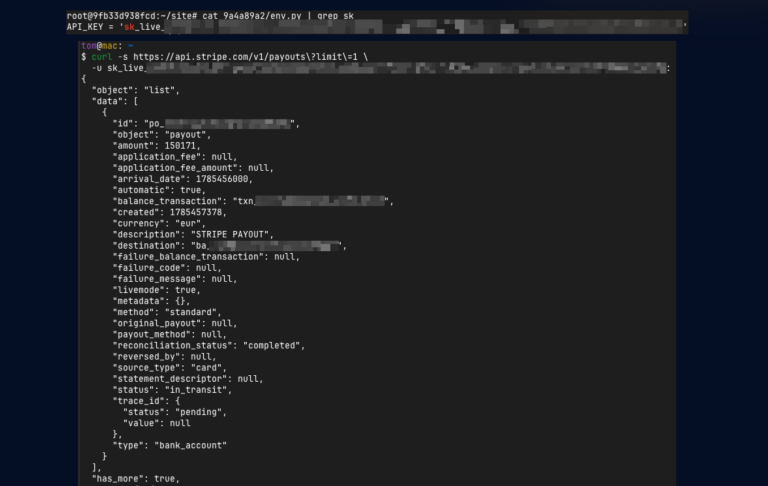
A scan found 28,000 exposed Git repositories leak credentials, API keys, and sensitive files. Learn how to secure your public web servers today.

Cursor AI editor found storing API keys and tokens in an unprotected SQLite database, allowing extensions to steal credentials silently. CVSS 8.2. No patch yet.

A medium-severity flaw (CVE-2025-3415) in Grafana Alerting exposes sensitive DingDing contact point URLs to viewers. Update to patch or disable the integration

Symantec found over 21 million Chrome extension users at risk due to hardcoded API keys and secrets, potentially leading to data manipulation and financial loss.

Learn how misconfigurations in Spring Boot Actuator can expose sensitive data and create opportunities for remote code execution in cloud environments.