 Do Son
Netskope uncovers a ClickFix macOS campaign that holds the UI hostage to steal system passwords, Keychains, and 200+ browser extensions.
AppleScript
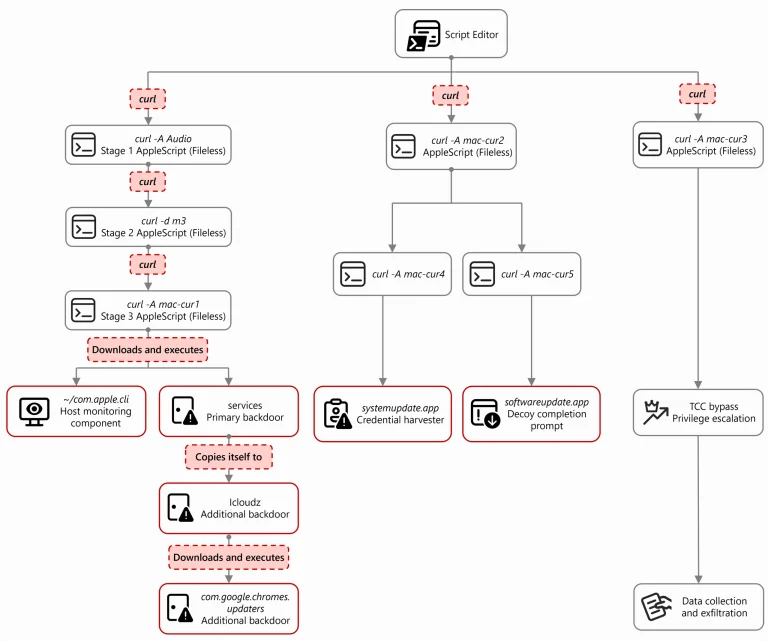
Microsoft uncovers Sapphire Sleet's macOS campaign. Using fake recruiters and AppleScript, they bypass TCC to steal crypto wallets, Telegram, and SSH keys.
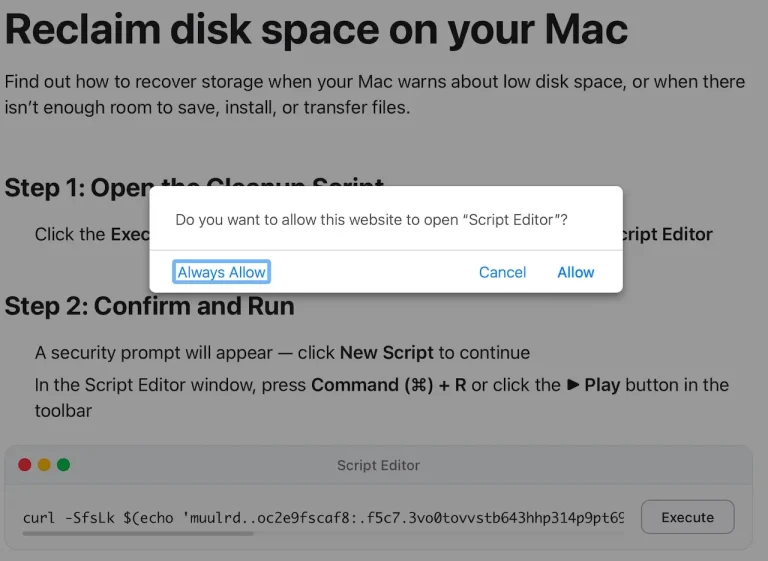
Jamf identifies a macOS ClickFix pivot: attackers now use the Script Editor to bypass Terminal scans and deliver Atomic Stealer. Learn how to stay protected.

Darktrace finds Mac malware using a fake "Compatibility Wizard" to trick users. The AppleScript attack bypasses TCC to drop a Node.js backdoor.

GlassWorm Wave 4 targets macOS developers via VS Code, using encrypted payloads and a 15-minute fuse to trojanize Ledger and Trezor wallet apps.

Researcher Mickey Jin uncovers CVE-2025-43530, a critical TCC bypass in macOS allowing attackers to hijack user data via accessibility tools.

A new macOS threat uses malicious AppleScript (.scpt) files, disguised as documents/updates, to bypass Gatekeeper and execute stealers like MacSync and Odyssey, exploiting user trust.

CYFIRMA uncovers "Odyssey Stealer," a new macOS malware using fake App Store prompts & typosquatting to steal crypto wallets, passwords, and browser data from Western users.