 Do Son
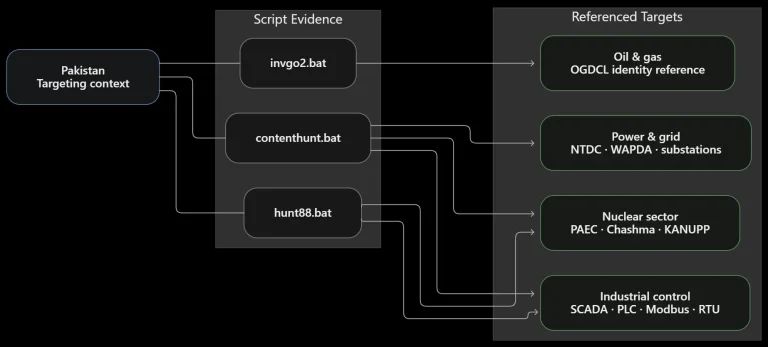
Researchers found an open server hosting a DoNot APT toolkit targeting Pakistan nuclear, power grid, and ICS networks with Inveigh and Go shells.
APT-C-35

The DoNot APT hit Bangladesh military targets with a fake officer biography. Cyderes traced a live, multi-stage implant to active C2 servers.

DoNot APT (APT-C-35) expands its cyber-espionage to a European foreign affairs ministry, using spear-phishing with Google Drive links to deliver the LoptikMod backdoor.

Uncover the latest campaign by the DONOT APT group targeting Pakistan's maritime and defense manufacturing sectors with advanced tactics.

Advanced Persistent Threat (APT) group APT-C-35, also known as DoNot Team, has been identified as one of the actors employing Rafel RAT