
 Do Son
NCSC warns high-risk individuals of Russian and Chinese state actors hijacking WhatsApp and Signal. Protect your chats with these essential 2026 defense tips.
APT31
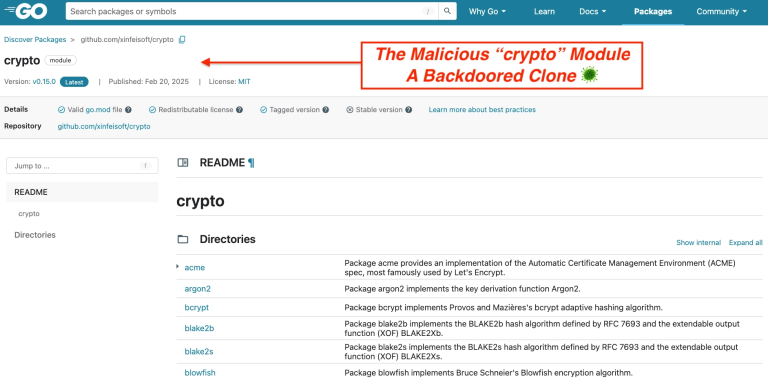
Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.

Unveiling a sophisticated cyber campaign targeting high-profile organizations in Southeast Asia. Discover the tactics and tools used by this China-based attacker.

Uncover the sophisticated cyberattack campaign known as 'Pacific Rim.' Discover how China-based threat groups target high-value infrastructure and government organizations

Discover the Rekoobe backdoor: a new cybersecurity threat with ties to APT31. Learn how it uses encrypted files and customized protocols to avoid detection in open directories.

Uncover the intricate cyber threat of GobRAT and Bulbature targeting edge devices worldwide. Learn how these malware variants have caused chaos in critical networks.
Learn about the advanced persistence and stealth techniques used by APT31 and APT27 in the EastWind cyberattacks targeting Russian organizations

Mandiant has revealed a concerning trend among China-linked cyber espionage groups: the use of ORB networks to enhance their espionage capabilities

a trend in China-linked cyberattacks: a sustained focus on compromising Operational Technology environments within critical infrastructure