 Do Son
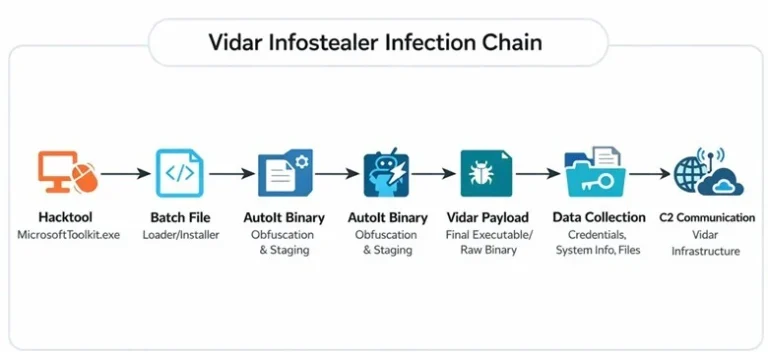
LevelBlue unmasks a stealthy Vidar Stealer campaign using AutoIt scripts and file renaming tricks to bypass EDR and harvest credentials. Is your system at risk?
AutoIt

A sophisticated Lumma Infostealer MaaS campaign targets users with pirated software installers. It uses NSIS/AutoIt scripts, Process Hollowing, and MEGA cloud to steal credentials from browsers and crypto wallets.

Horabot malware targets Latin America with fake invoices, hijacking Outlook to spread phishing emails and steal data via stealthy scripting.
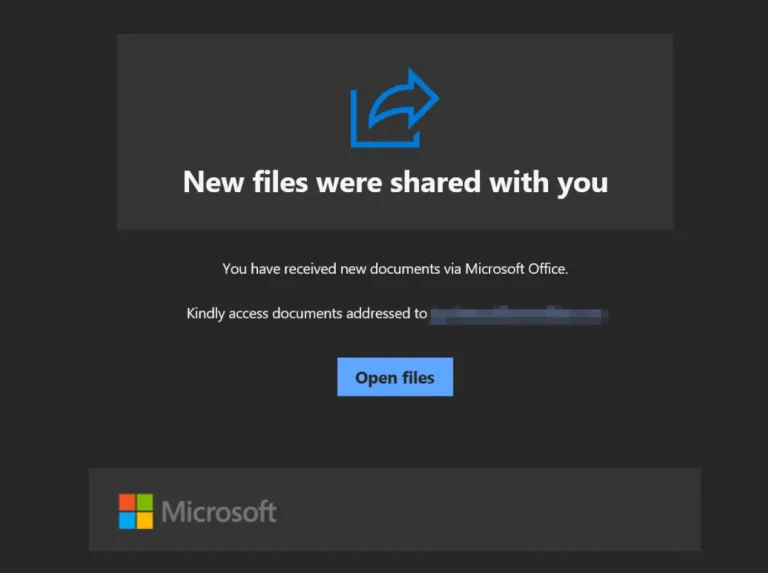
Unveiling a new malicious SharePoint impersonation campaign delivering Xloader malware. Learn how this sophisticated attack takes advantage of brand impersonation and advanced process injection.

Discover the new attack method used by cybercriminals: StealC malware. Learn how this malicious software steals user credentials through web browsers.