
 Do Son
Operation DualScript uses parallel execution to bypass defenses, hijacking crypto wallets and banking data via RetroRAT and clipboard swapping.
banking malware
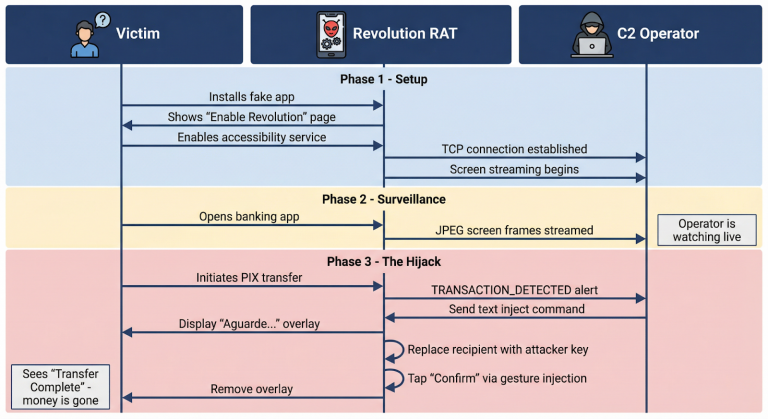
Zimperium's zLabs exposes PixRevolution, a novel Android banking trojan using real-time surveillance to hijack Brazil's PIX instant payments.

Frogblight, a new Android banking Trojan, is targeting Turkey via smishing with fake e-government apps. It uses WebView to steal credentials and is linked to the Coper MaaS family. It is being actively developed.

A unique Android banking trojan, FvncBot, targets mBank (Poland) customers. It uses HVNC and H.264 to stream screens and performs web-inject attacks via FCM/WebSocket C2.

The new Sturnus Android banking trojan bypasses end-to-end encryption on WhatsApp & Signal and enables full device takeover for hidden financial fraud.

The Datzbro Android Trojan is targeting seniors via fake Facebook groups and AI content. The hybrid malware can remotely control devices and steal banking credentials.

Carbanak malware, previously utilized for stealing banking data, is now employed by the cybercriminal group FIN7 for remote control