 Do Son
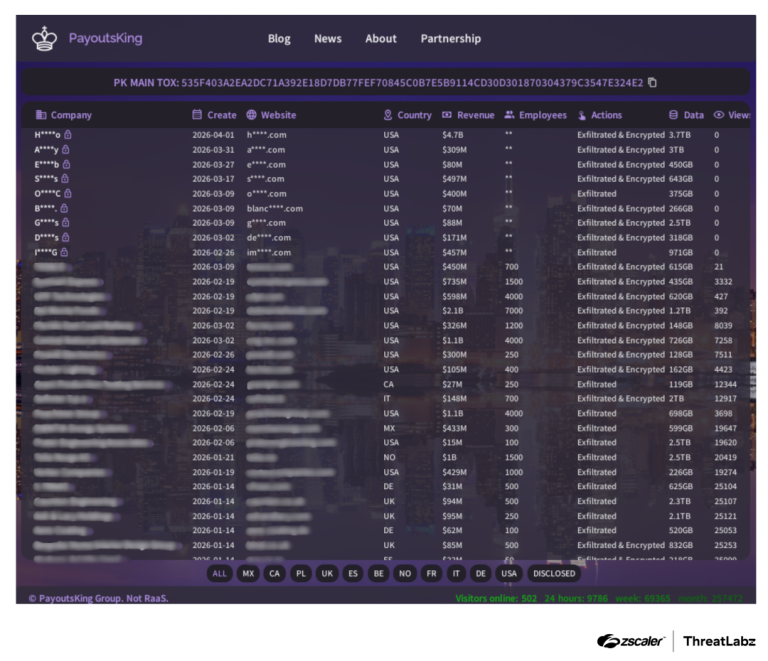
Payouts King, the successor to BlackBasta, uses vishing and direct syscalls to bypass EDR and strike global targets. Learn how to defend your enterprise.
BlackBasta

A new malware loader, CountLoader, is linked to Russian ransomware groups. The malware uses phishing lures impersonating the Ukrainian National Police to deliver payloads.

A JPCERT/CC report reveals a new attack campaign using CrossC2 and a custom loader to compromise both Linux and Windows systems.
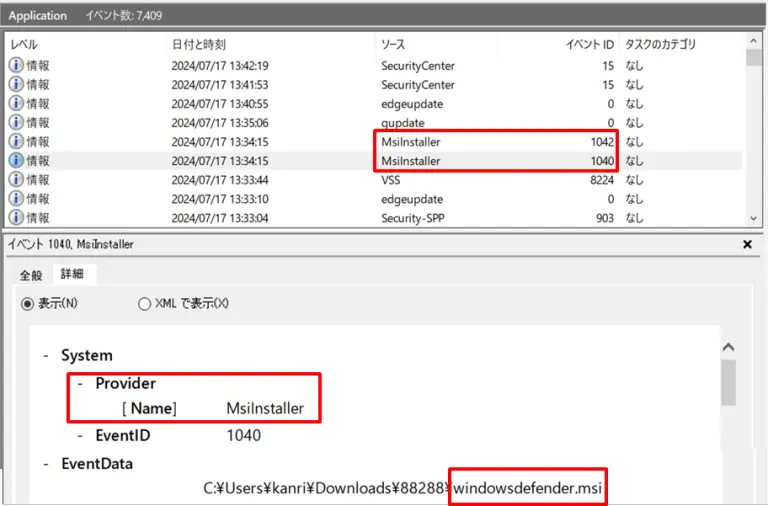
Discover how Windows Event Logs can be a powerful tool in the fight against human-operated ransomware. Learn how to detect and mitigate these evolving threats.

Notably, DiceLoader has been actively used since 2021, with the malware often delivered via a PowerShell script.
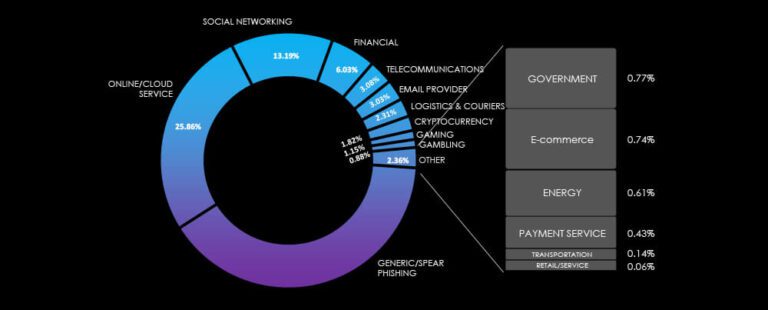
CYFIRMA Industries Report offers an illuminating look into the current state of cyber threats, in the professional goods & services industry