 Do Son
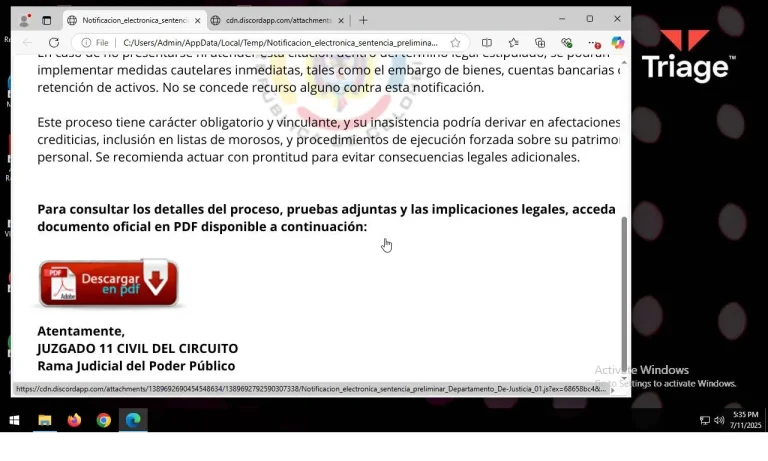
A new report reveals the Blind Eagle hacking group is using spearphishing and commodity RATs to conduct cyber espionage against Colombian government and private sector targets.
Blind Eagle

Trustwave exposes Blind Eagle (APT-C-36) leveraging exposed infrastructure and VBS malware in phishing campaigns, targeting Colombian banks with blatant disregard for concealment.

Censys uncovers "sostener.vbs," an obfuscated VBScript launching a multi-stage RAT delivery pipeline, affecting dozens and potentially linked to Blind Eagle APT.

Explore how the Blind Eagle group has evolved since 2018, employing advanced tactics like Remote Access Trojans to conduct cyber espionage.
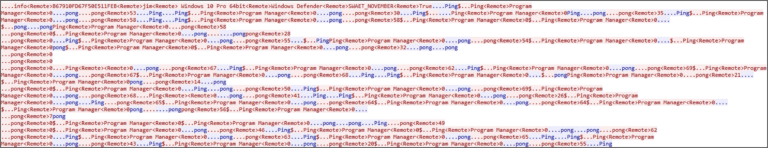
PhantomControl, a chameleon in the digital world, has previously been associated with the Blind Eagle threat actors