 Do Son
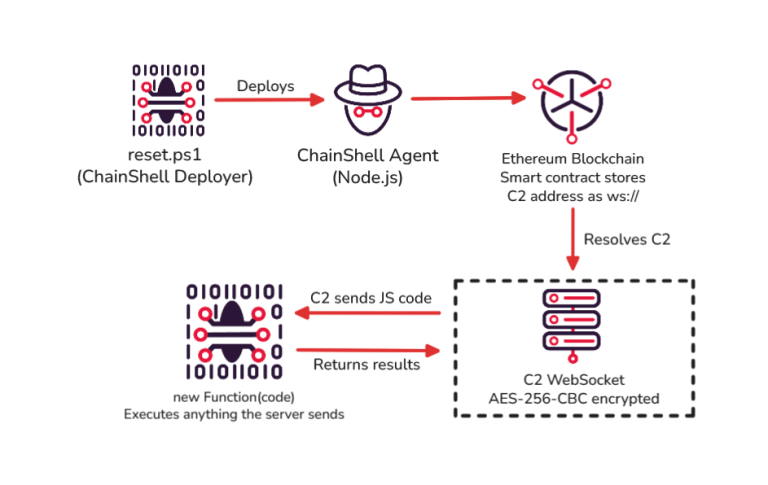
Iranian state actor Muddy Water adopts CastleRAT and ChainShell to hijack browsers and bypass MFA invisibly. A professional-grade shift in APT strategy.
CastleRAT

GrayBravo MaaS uses CastleRAT to target logistics/hospitality. The RAT hides its C2 by using Steam Community profiles as Dead Drop Resolvers, bypassing network monitoring.

A new C-compiled RAT, CastleRAT, uses Steam Community pages to hide its C2. The malware deploys advanced features like UAC Bypass, screen capture, and clipboard hijacking for espionage.

Darktrace exposed TAG-150, a new MaaS operator compromising 469+ US devices in months. The group uses ClickFix to trick victims into running malicious PowerShell that deploys the CastleLoader/CastleRAT backdoor.

A new report reveals TAG-150, a sophisticated new threat actor with evolving malware and a resilient multi-tiered infrastructure, including a new RAT called CastleRAT.