 Do Son
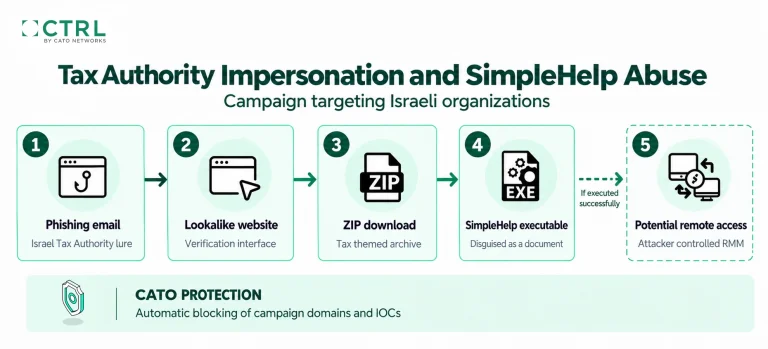
Cato CTRL exposed the MuddyWater SimpleHelp campaign in Israel using tax lures. Learn how the MuddyWater SimpleHelp campaign abuses RMM tools.
Cato CTRL

Cato CTRL details a new SilverFox ValleyRAT campaign in Japan using three BYOVD drivers and DLL sideloading to kill security tools.

Cato CTRL intercepts "TencShell," a new stealth malware derived from open-source Rshell. Attackers use third-party access to breach networks!
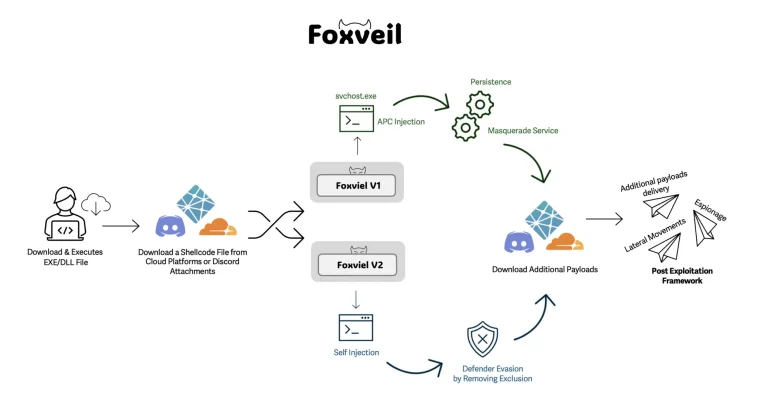
Cato CTRL discovers Foxveil, a new malware loader abusing Cloudflare, Netlify & Discord to bypass defenses. Active since Aug 2025. Learn the signs.