 Do Son
CERT/CC details six FrodoBots EarthRover vulnerabilities, including root remote code execution via MQTT. Patch status, risks and mitigations.
CERT/CC
CERT/CC warns of a critical Xerj authentication bypass tracked as CVE-2026-97406 that lets attackers mint persistent tokens without passkeys.
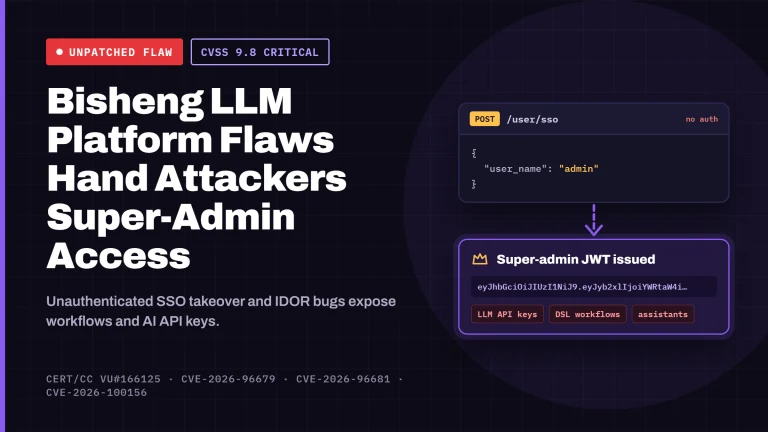
CERT/CC disclosed three DataElement Bisheng vulnerabilities (CVE-2026-96679, CVE-2026-96681, CVE-2026-100156) allowing unauthenticated admin takeover.
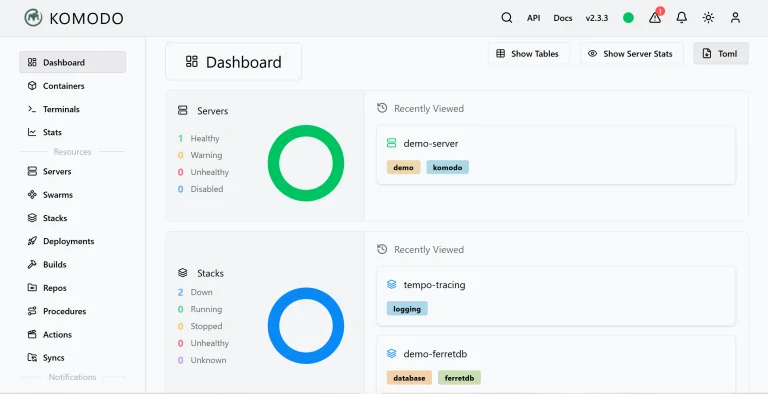
Patch CVE-2026-110005 (CVSS 9.9), a critical Komodo Periphery vulnerability allowing authenticated users to run arbitrary OS commands as root on the host.
An unpatched Shopware vulnerability, CVE-2026-104937, lets stored XSS steal admin tokens and lead to RCE in Shopware 6.7. Restrict media uploads now.
CERT/CC lists 11 unpatched Thelia vulnerabilities, including remote code execution flaws in versions 2.6.0, 2.6.1 and 3.0.0. Lock down admin access now.
Five RDK-B WebUI vulnerabilities let attackers bypass authentication and gain admin access on broadband gateways. No patch is available yet.

Six SGLang vulnerabilities include unauthenticated RCE via CVE-2026-15969, plus data and model-weight theft. No patch exists yet.
The Arris BGW210-700 vulnerability, CVE-2026-16771, is an authentication bypass in AT&T's gateway. A LAN user can read the WiFi password.

CERT/CC warns of a Plane authorization bypass, CVE-2026-15342. It lets users reach other workspaces' files, and no patch exists yet.
CERT/CC discloses six Logto vulnerabilities, including CVE-2026-15611 and CVE-2026-15616, that enable SSO authentication bypass and MFA skipping.
CVE-2026-14890 is an unpatched SGLang vulnerability enabling unauthenticated remote code execution through pickle deserialization. Restrict access now.
A Haskell TLS vulnerability (CVE-2026-9648) lets attackers bypass X.509 NameConstraints to impersonate domains. Update crypton-x509-validation to 1.9.1.

Urgent: dnsmasq patches 6 critical flaws (CVE-2026-2291+) enabling DNS poisoning and root access. Update your router firmware to version 2.92rel2 now!
Urgent: Casdoor IAM platform hit by critical file write flaw (CVE-2026-44213). Attackers can bypass sandboxes to overwrite databases and gain host access.

Kyverno (CVE-2026-4789) faces an unpatched SSRF flaw in its CEL HTTP functions, allowing attackers to bypass K8s namespaces. Secure your cluster now!
CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.

Critical Redmi Buds flaws (CVE-2025-13834) allow data theft and device crashes via Bluetooth. "Heartbleed"-style bug has no patch. Disable Bluetooth now.

CVE-2025-14026: Attackers can reconstruct a crippled Python runtime in Forcepoint DLP to execute arbitrary code. Update now to remove the vulnerability.

Three specification-level flaws in PCIe 6.0 IDE allow an attacker with physical access to inject stale/corrupted data into secure streams. Firmware updates are required to fix the data integrity risk.

CERT/CC warned that Tenda 4G03 Pro/N300 routers are exposed to an unpatched RCE flaw (CVE-2025-13207). Authenticated attackers can execute root-level commands via web requests due to insecure input handling.

A critical RCE flaw in DrayTek Vigor routers can be exploited without authentication via the web interface if EasyVPN is enabled, granting remote root access.