 Do Son
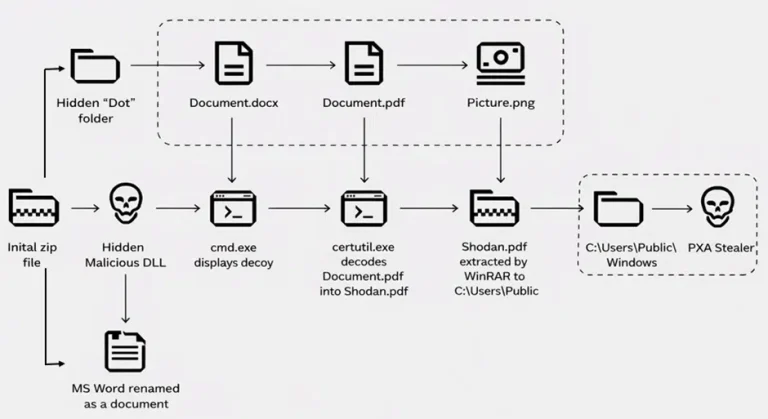
PXA Stealer activity surges in Q1 2026, targeting global finance. Learn how this Python-based malware uses Telegram and LOLBins to hijack crypto and banking data.
Certutil
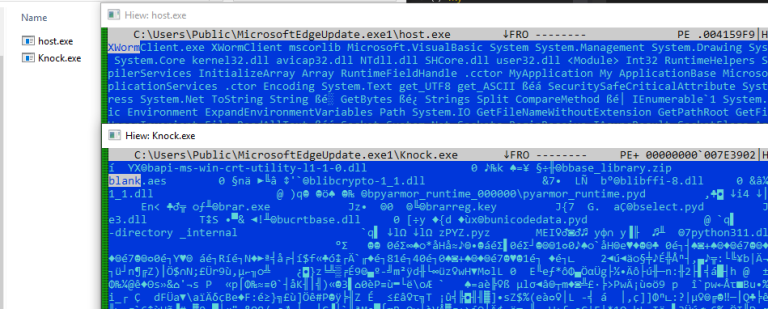
Splunk unmasks BlankGrabber: a modular Python info stealer using Discord and GitHub to swipe credentials and Discord tokens. Learn how to stay protected.

Kimsuky APT is using a Themes.js JavaScript loader and certutil LOLBIN to gain minute-by-minute persistence via a Windows Scheduled Task. The APT is targeting think tanks for espionage.