 Do Son
A Microsoft Teams vishing campaign tracked as STAC4749 hit dozens of North American firms and deployed Chaos ransomware in under 17 hours.
Chaos Ransomware
Cisco Talos found msaRAT malware, a Rust RAT from the Chaos ransomware group that hides C2 traffic inside headless Chrome and Edge sessions.
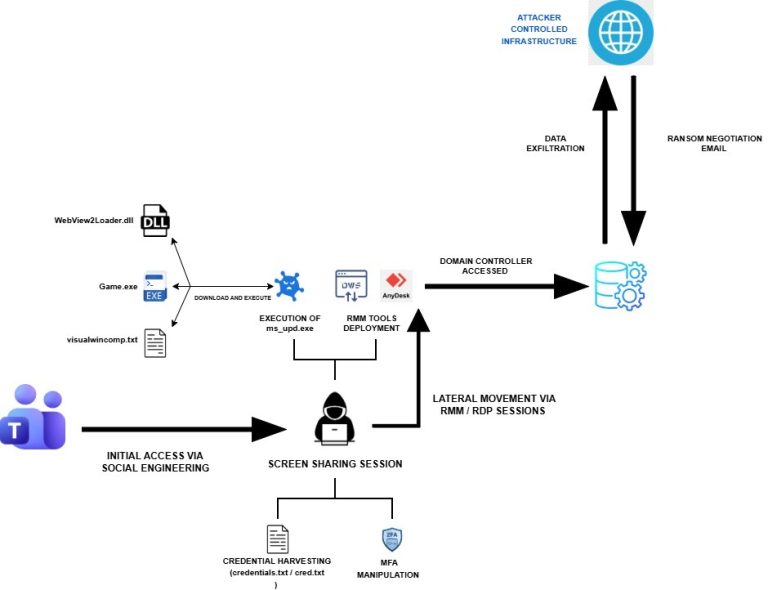
Rapid7 unmasks Iranian APT MuddyWater using a Chaos ransomware "false flag" to hide state-sponsored espionage. See how they bypassed MFA via MS Teams.

FortiGuard uncovered Chaos-C++, a dangerous new ransomware strain. It deletes file content over 1.3 GB and uses clipboard hijacking to steal Bitcoin during payments.

Cisco Talos reveals "Chaos," a new RaaS operation likely formed by former BlackSuit members, using vishing and Quick Assist to conduct big-game hunting and double extortion campaigns.

Spectra Ransomware, an evolution of Chaos, encrypts Windows files with AES-RSA, demands $5,000 in Bitcoin, and uses double extortion tactics with system evasion