 Do Son
A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.
Cofense

The Lone None group uses fake copyright notices to deliver a new stealer malware that focuses on crypto theft via clipboard replacement and utilizes Telegram for C2.

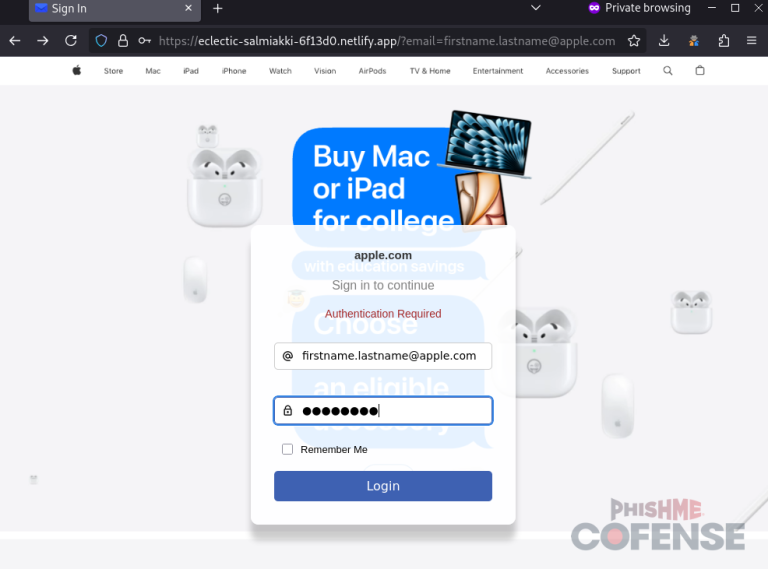
Cofense Intelligence reports a new phishing tactic using blob URIs to bypass Secure Email Gateways. Attackers use these local URIs to hide phishing pages.

A new "Pick Your Poison" phishing campaign tricks users into choosing between having their credentials stolen or infecting their systems with malware. Cofense analysis reveals how this double-edged attack uses files.fm to deliver malicious payloads.