 Do Son
DOUBLECUP is a new Russian ClickFix Loader-as-a-Service that drops CountLoader and the DeviceManager RAT using steganography and EtherHiding.
CountLoader
McAfee Labs exposes a massive CountLoader campaign using EtherHiding and AMSI bypass to drop stealthy cryptocurrency clippers. Secure your assets!

Silent Push found AdaptixC2, an open-source pen-testing framework, is now used by Russian cybercriminals and Akira RaaS. The developer's Russian-language activity suggests strong ties to the threat ecosystem.

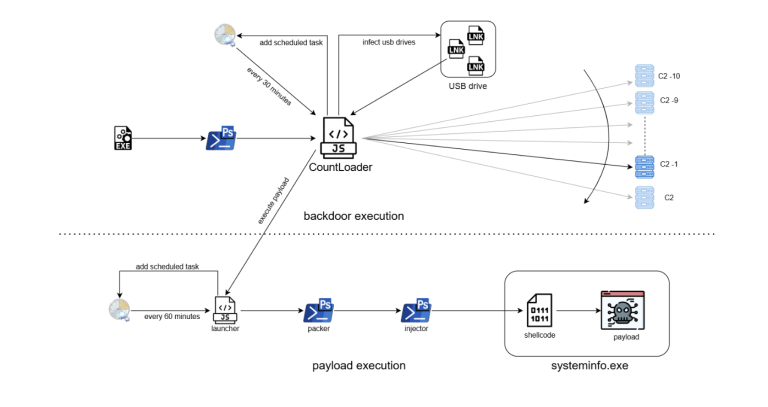
A new malware loader, CountLoader, is linked to Russian ransomware groups. The malware uses phishing lures impersonating the Ukrainian National Police to deliver payloads.