 Do Son
A new npm supply chain attack hijacked keyv and dozens of packages, spreading Shai-Hulud malware that steals cloud and CI/CD secrets. Rotate keys now.
credential stealer

A massive PyPI supply chain attack has hit developers. Learn how Socket malware detection uncovered the Hades cluster stealing cloud credentials.
Arctic Wolf warns of a new FortiClient EMS exploitation campaign using CVE-2026-35616 to deploy the stealthy EKZ Infostealer malware.

Urgent: 84 TanStack npm packages hijacked to harvest GitHub Actions secrets. Over 12M weekly downloads impacted. Audit your CI/CD pipelines and rotate tokens.
SAP developers are under attack. A surgical credential stealer hijacks CI/CD runners and cloud tokens via npm preinstall hooks. Rotate all secrets immediately.
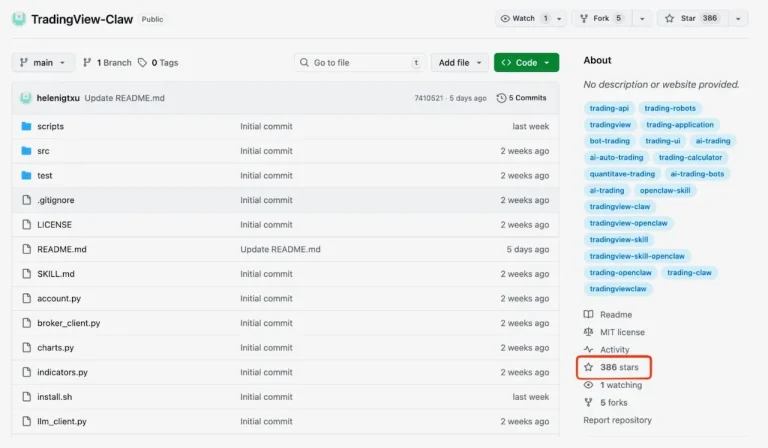
Jamf Threat Labs uncovers GhostClaw, a macOS threat exploiting GitHub stars and AI workflows to steal credentials. Protect your dev environment today!

North Korea's "Contagious Interview" campaign uses DriverFixer0428 to steal macOS credentials via fake prompts and Dropbox C2. Stay alert!

Cyfirma uncovers "Octalyn Forensic Toolkit," a GitHub-hosted "educational" tool that's actually a modular credential stealer exfiltrating data via Telegram.

OtterCookie malware by North Korea-linked WaterPlum group evolves to target Chrome, MetaMask, and system files on both Windows and macOS platforms.