
 Do Son
GenieLocker ransomware hits Russia's manufacturing sector on Windows, Linux, and ESXi. Linked to the Toy Ghouls group, it leaves no ransom note.
Cross-Platform Malware
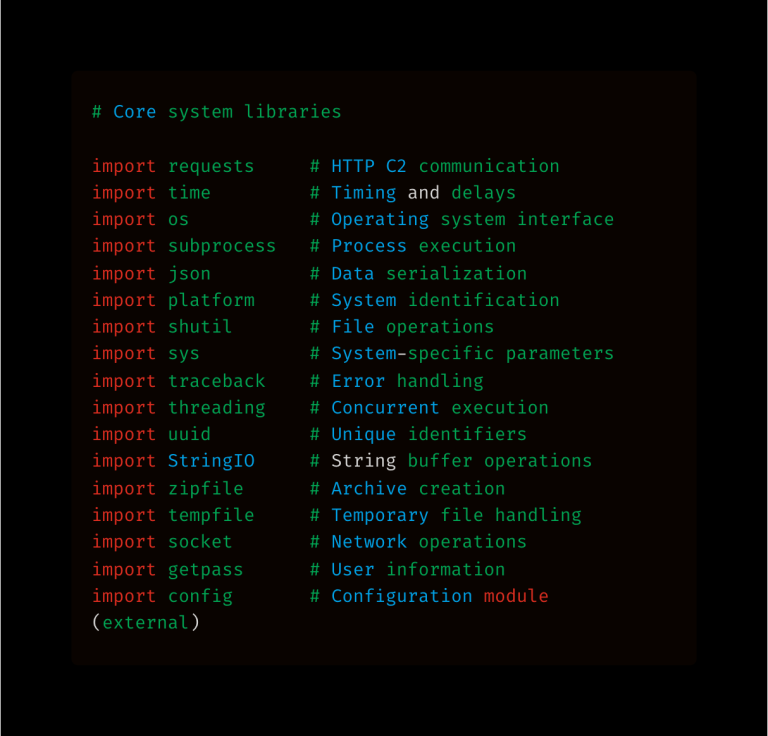
K7 Labs uncovers a stealthy Python-based RAT disguised as an ELF binary. Features adaptive beaconing and anti-forensics to stay hidden. Read the analysis.

Netskope exposed a Python RAT (Nursultan Client) disguised as a Minecraft tool. It uses the Telegram Bot API for C2 to steal Discord tokens, credentials, and capture screenshots on Windows, Linux, and macOS.