 Do Son
Apache Wicket vulnerabilities: a security update fixes 19 flaws, including CVE-2026-84170 upload DoS and XSS bugs. Upgrade to 8.20.0, 9.25.0 or 10.12.0.
Cross-Site Scripting
Eight unpatched Siemens S7-1500 vulnerabilities enable cross-site scripting in the PLC web server, rated up to CVSS 9.4. Apply Siemens mitigations now.
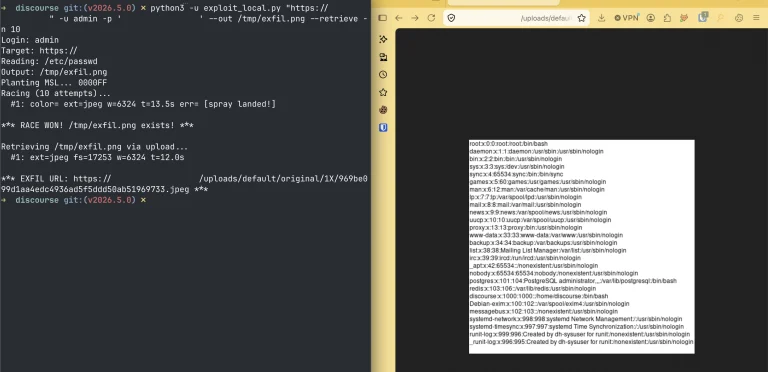
Two Discourse vulnerabilities, CVE-2026-55674 and CVE-2026-55420, enable cache poisoning XSS and server file reads. Patch to the fixed releases now.
IBM fixes 23 IBM DataPower Gateway vulnerabilities, including critical RCE flaws CVE-2026-15762 and CVE-2026-16340. Upgrade to 11.0.0.3 now.
An active WordPress XSS campaign exploits Ninja Forms flaw CVE-2026-94504 and CVE-2026-93836 to plant hidden admin accounts. Patch now.
A JupyterLab Desktop vulnerability, CVE-2026-102530 (CVSS 9.4), turns a malicious server URL into remote code execution. Update to 4.6.2-1 now.
A critical Rancher XSS vulnerability tracked as CVE-2026-88804 exposes admin sessions. Update your clusters immediately to prevent system compromise.
The WordPress 7.1.1 security release fixes 11 flaws, including stored cross-site scripting and path traversal. Update your sites immediately.

WordPress 7.0.3 fixes CVE-2026-64638, a pre-auth XSS on the login screen that can escalate to remote code execution. CVSS 8.9. Update now.
Progress patched three MOVEit Transfer flaws, including a stored XSS bug (CVE-2026-11903). No exploitation is confirmed. Update now.
The GitLab patch release fixes 8 flaws, including a high-severity cross-site scripting bug (CVE-2026-6896). Update to 19.1.2 now.

New updates patch critical Spring security vulnerabilities, mitigating cross-site scripting and server-side request forgery risks across multiple versions.
Learn about the Apache ECharts XSS vulnerability (CVE-2026-45249) in the Lines series tooltip rendering logic and find out how to secure your code.
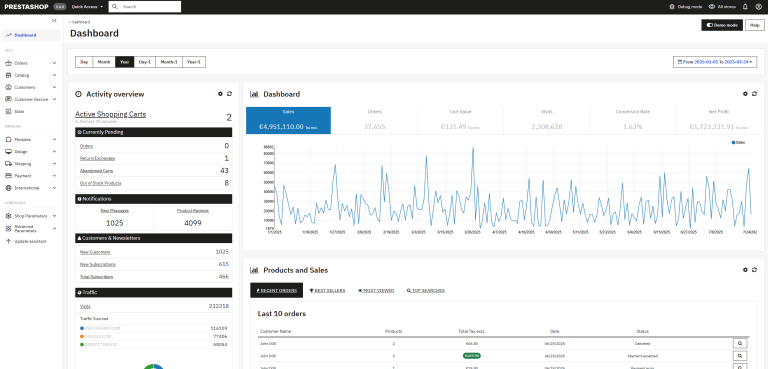
Urgent: PrestaShop patches a 9.3 severity XSS flaw (CVE-2026-44212) that allows unauthenticated attackers to hijack your store's back office. Update now!

A critical 9.6 CVSS vulnerability in jsPDF (CVE-2026-31938) allows attackers to inject malicious scripts via XSS. Update to version 4.2.1 immediately.

An 8.6 CVSS Angular XSS vulnerability (CVE-2026-32635) bypasses built-in sanitization via i18n attributes. Patch your web applications immediately.
A critical 9.6 CVSS XSS vulnerability (CVE-2025-40943) in Siemens SIMATIC S7-1500 CPUs allows attackers to inject malicious code via trace files.
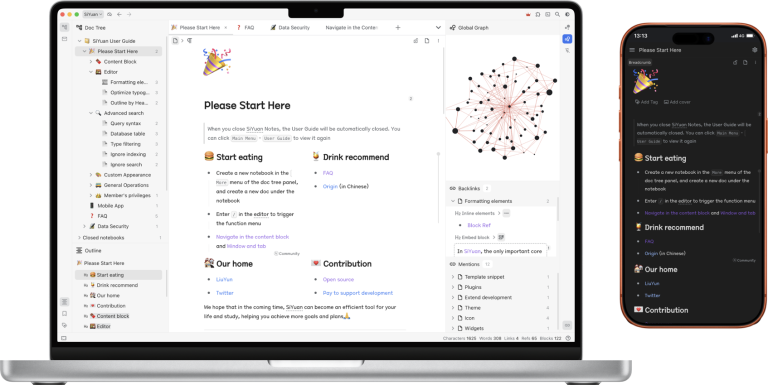
A critical 9.3 CVSS reflected XSS flaw (CVE-2026-29183) in SiYuan's dynamic icon API lets attackers steal private notes via SVG injection. Update now.

A critical 9.3 CVSS XSS vulnerability (CVE-2026-29191) in ZITADEL's SAML endpoint allows unauthenticated 1-click account takeover. Upgrade immediately.

Mozilla Firefox 148 launches the standardized Sanitizer API. Discover how the new setHTML() method systematically strips XSS attacks to protect web users.

IceWarp urges immediate patching for critical flaws allowing unauthorized server access, XSS, and arbitrary file reading. Update your instances today.