 Do Son
The Binance hack hit USD 6.34B via a fake job interview, an abused AI tool and EIP-7702 delegation. The FBI points to North Korea.
Crypto theft
SlowMist warns the FomoPeek malware hides an iOS kernel exploit that steals crypto private keys and seed phrases. Update iOS and move funds now.
Researchers discovered malicious Packagist themes iOS spyware infecting unpatched iPhones. This spyware targets crypto wallets and steals device data.
ReliaQuest found the Gryxa toolkit, AI-built malware that steals crypto credentials and spies on how defenders try to remove it across 324 hosts.

The COLDCARD seed flaw theft has climbed to 1,367 BTC across three attack waves and 4,585 wallets, with the third wave using harder-to-trace P2WSH addresses.
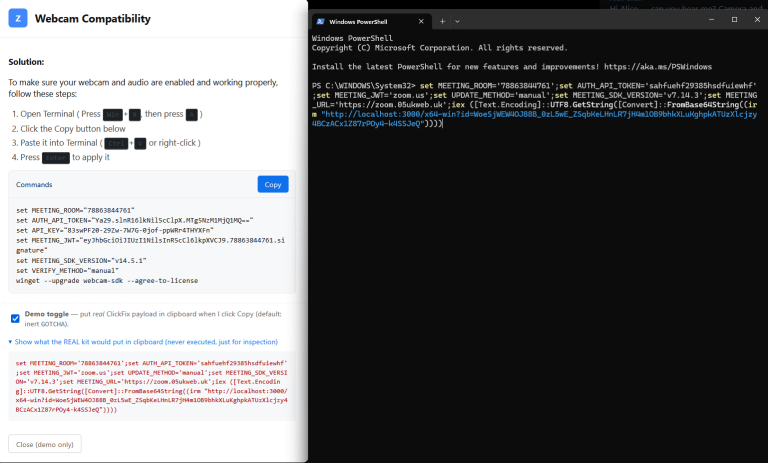
JUMPSEC analyzed the BlueNoroff phishing kit's source code. The DPRK ClickFix attack fakes Zoom and Teams calls to profile and drain crypto wallets.

McAfee Labs exposes a massive CountLoader campaign using EtherHiding and AMSI bypass to drop stealthy cryptocurrency clippers. Secure your assets!
Netskope exposes Hologram: a red-team-grade malware framework targeting OpenClaw AI users with CLR injection and WinLogon hijacking to steal crypto wallets.
Job seekers beware: The JobStealer trojan poses as video meeting apps to hijack 300+ crypto wallets and Telegram data. Learn how to spot this 2026 threat.
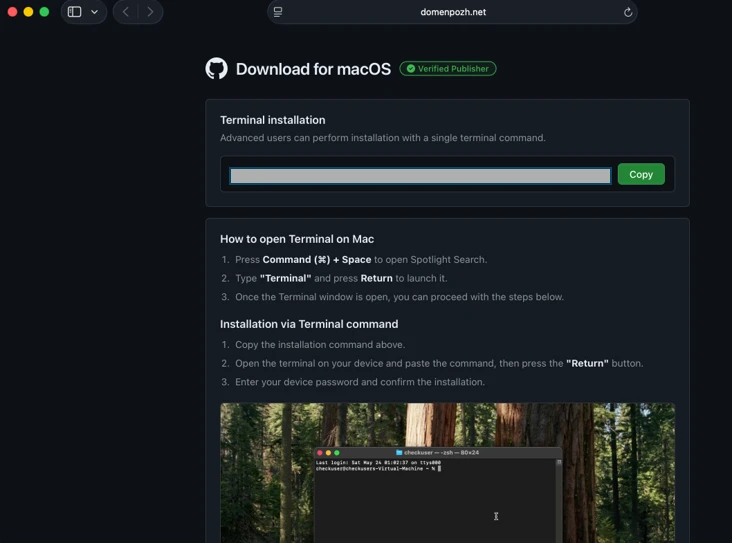
Microsoft reveals a macOS ClickFix campaign using fake "fixes" to trick users into running Terminal commands that bypass Gatekeeper and steal crypto wallets.
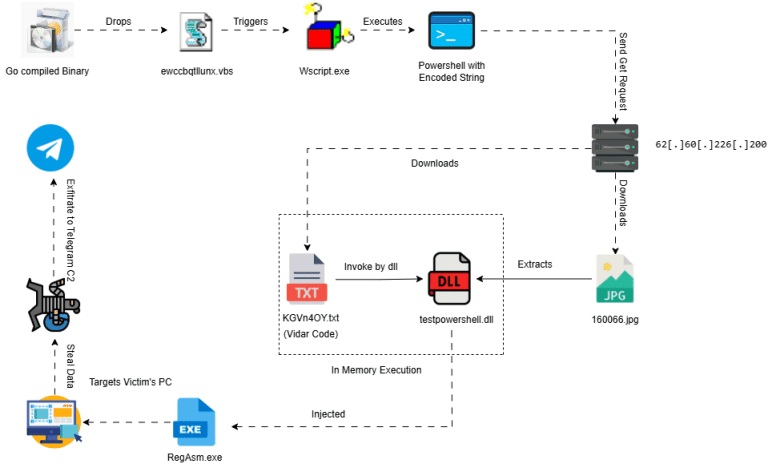
Vidar infostealer evolves into a fileless 2026 threat. From fake CAPTCHAs to "Claude Code" leaks, see how it steals crypto and passwords via Telegram C2.
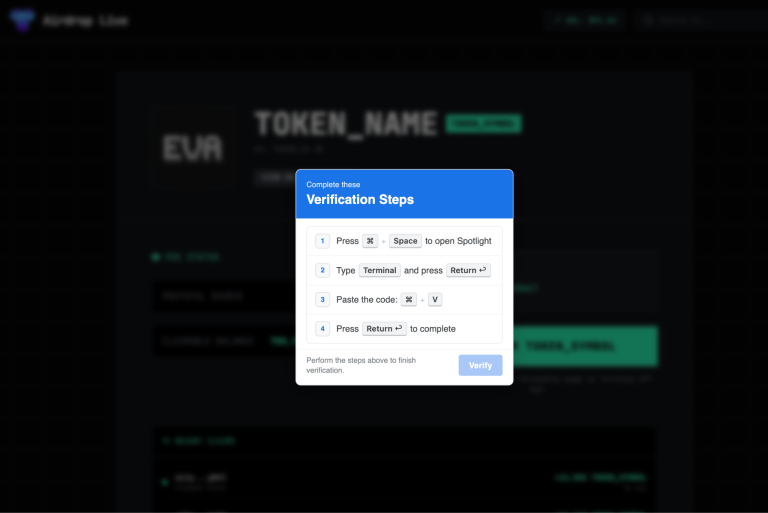
Netskope uncovers a ClickFix macOS campaign that holds the UI hostage to steal system passwords, Keychains, and 200+ browser extensions.

North Korea's UNC1069 uses fake video calls and "ClickFix" prompts to drain crypto assets and record victims for deepfakes. Audit your meetings now!
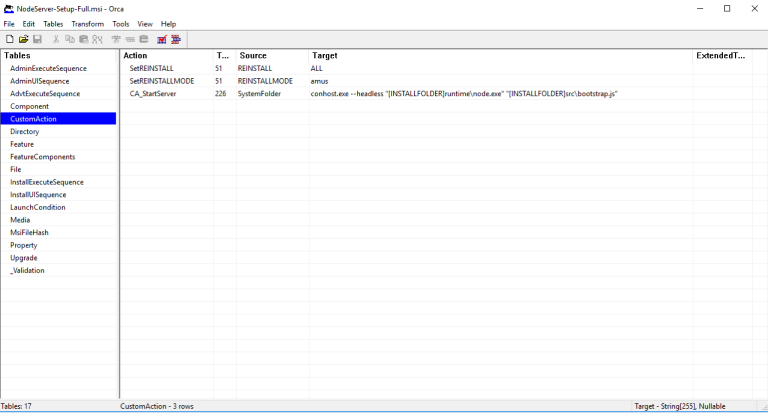
Netskope uncovers a Node.js-based ClickFix campaign using gRPC over Tor for stealthy crypto theft. A leaked file exposed their entire MaaS backend.
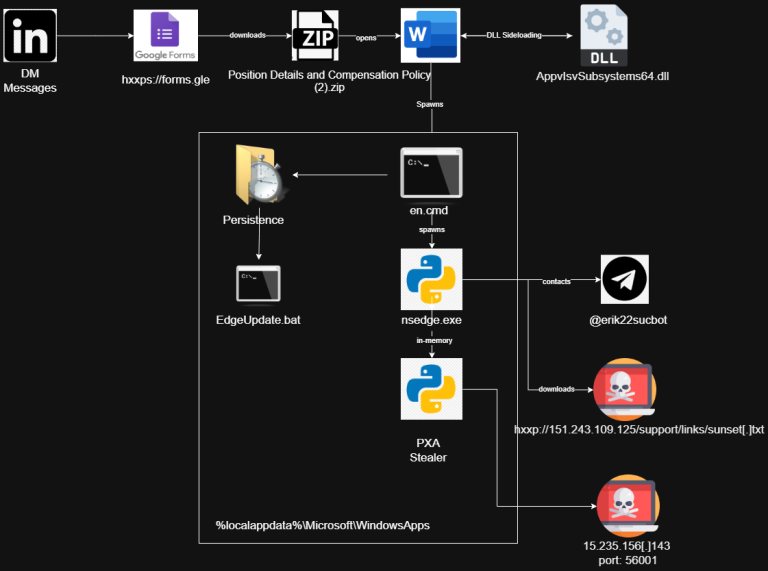
LinkedIn job seekers are being targeted by a sophisticated Vietnam-based group using PXA Stealer. This 100MB malware bypasses MFA and drains crypto wallets.

Operation DualScript uses parallel execution to bypass defenses, hijacking crypto wallets and banking data via RetroRAT and clipboard swapping.

North Korean group NICKEL ALLEY targets tech pros with "Contagious Interview" scams. Using fake job tests and RATs, they steal crypto and corporate access.

LevelBlue uncovers MioLab (Nova), a premium macOS MaaS targeting crypto wallets, Keychains, and Apple Notes. Protect your BIP39 seeds and Mac today.

Google Threat Intelligence uncovers "Coruna", a repurposed iOS exploit kit now used by state-sponsored and financially motivated hackers to steal crypto.
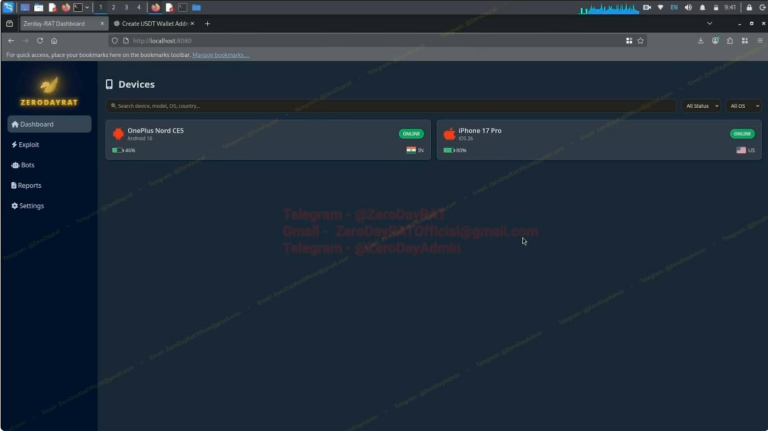
ZeroDayRAT mobile spyware is sold on Telegram. It offers full remote control of Android & iOS devices, including camera streaming & crypto theft.

New LTX Stealer malware abuses Node.js & Inno Setup to bypass antivirus. This $10 tool steals browser passwords & crypto wallets. Stay alert.

Rublevka Team's "scam-as-a-service" has stolen $10M+ in crypto. Their automated Solana drainers target Phantom & Solflare wallets. Don't be next.