
 Do Son
Understand the impact of the CVE-2024-45409 vulnerability that allows bypassing SAML authentication and gaining unauthorized access.
CVE-2024-45409

Protect your GitLab installations from a critical vulnerability. Learn about CVE-2024-45409, a security flaw in SAML authentication, and upgrade to safeguard your data.

Stay informed about the urgent GitLab vulnerability update. Learn how to address the critical CVE-2024-45409 flaw that exposes instances to potential security breaches.
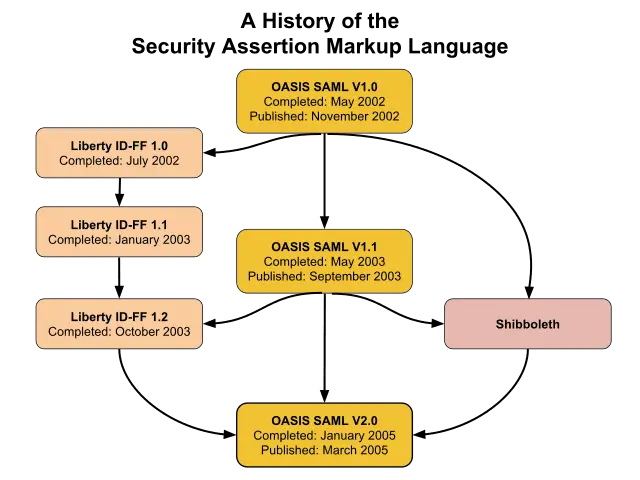
Find out about the high-risk security vulnerability CVE-2024-45409 in Ruby SAML. Understand the potential risks of unauthorized access due to this authentication bypass.