
 Do Son
Dr. Tube’s AI-assisted Bissa scanner exploited 900+ companies using React2Shell (CVE-2025-55182) to steal 30,000 .env files. See the AI-led attack workflow.
CVE-2025-55182

Cisco Talos uncovers UAT-10608, an automated campaign using "NEXUS Listener" to harvest Next.js credentials via React2Shell. Patch your cloud tokens now!
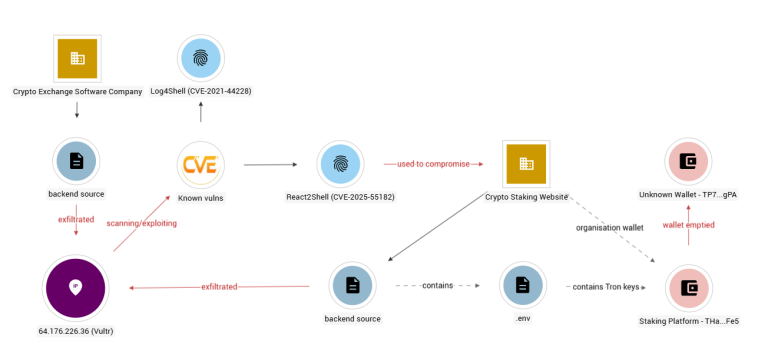
Ctrl-Alt-Intel exposes a suspected DPRK campaign using an 'Amazon Kill Chain' and React2Shell to systematically breach crypto exchanges and steal code.

Darktrace detects AI-generated "vibecoding" malware exploiting React2Shell (CVE-2025-55182). Attackers use AI to deploy XMRig miners on Docker.

Critical React flaw CVE-2025-55182 (CVSS 10.0) under mass exploitation. Two IPs drive 56% of attacks deploying miners & shells. Upgrade to v19.0.1+ now.

Threat actor uses React2Shell to deploy Sliver C2 on FortiWeb devices, using a Bangladesh Airforce decoy to target govt and financial sectors.

CloudSEK uncovers the RondoDoX botnet's expansion into enterprise Next.js apps via the React2Shell exploit, alongside global IoT compromises.

PCPcat exploited Next.js/React flaws to hijack 59,128 servers in just 48 hours. Protect your cloud credentials and patch CVE-2025-55182 now!

ASEC warns of EtherRAT, a multi-stage crypto-stealer exploiting the React2Shell flaw. It uses Node.js and Ethereum for stealthy C2. Patch now!
React2Shell: Max-Score RCE (CVSS 10.0) Triggers Widespread Exploitation by Espionage Groups & Miners

React2Shell: Max-Score RCE (CVSS 10.0) Triggers Widespread Exploitation by Espionage Groups & Miners
A critical RCE (CVSS 10.0) in React Server Components (CVE-2025-55182) is under widespread exploitation by China-nexus groups deploying MINOCAT and HISONIC backdoors, plus XMRig miners.

A Critical RCE (CVSS 10.0) flaw, React2Shell, in React/Next.js's Flight protocol allows unauthenticated system takeover. North Korean and Chinese state actors are actively exploiting the deserialization bug.

A sophisticated new malware, EtherRAT, leverages Ethereum smart contracts for covert C2 (EtherHiding) 48 hours after the React2Shell (CVSS 10.0) flaw. Analysis shows ties to North Korean APTs.

Amazon exposed Chinese APTs exploiting the React2Shell zero-day (CVE-2025-55182, CVSS 10.0) hours after disclosure. Earth Lamia and Jackpot Panda are actively targeting unpatched Next.js servers for reconnaissance.