Skip to content
October 12, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • CVE-2026-55040

CVE-2026-55040

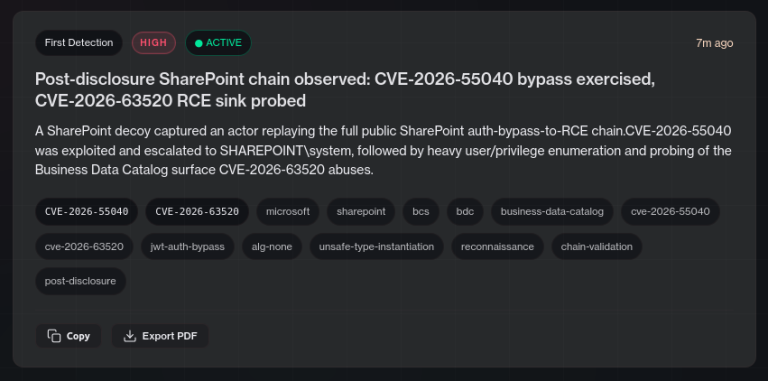
CVE-2026-63520: SharePoint RCE Chain Probed in the Wild, PoC Public SharePoint RCE vulnerability PoC diagram showing CVE-2026-63520 exploitation
  • Vulnerability Report

CVE-2026-63520: SharePoint RCE Chain Probed in the Wild, PoC Public

Do Son August 25, 2026 0
Security researchers have released full technical details and proof-of-concept exploit code for a critical SharePoint RCE vulnerability...
Read More Read more about CVE-2026-63520: SharePoint RCE Chain Probed in the Wild, PoC Public
CISA KEV Adds Four Exploited Flaws in SharePoint, vCenter CISA KEV Catalog adds four exploited vulnerabilities in SharePoint VMware vCenter macOS and Windows IKE
  • Vulnerability Report

CISA KEV Adds Four Exploited Flaws in SharePoint, vCenter

Do Son August 19, 2026 0
TL;DR CISA added four vulnerabilities to its Known Exploited Vulnerabilities Catalog on August 18, 2026. Each entry...
Read More Read more about CISA KEV Adds Four Exploited Flaws in SharePoint, vCenter
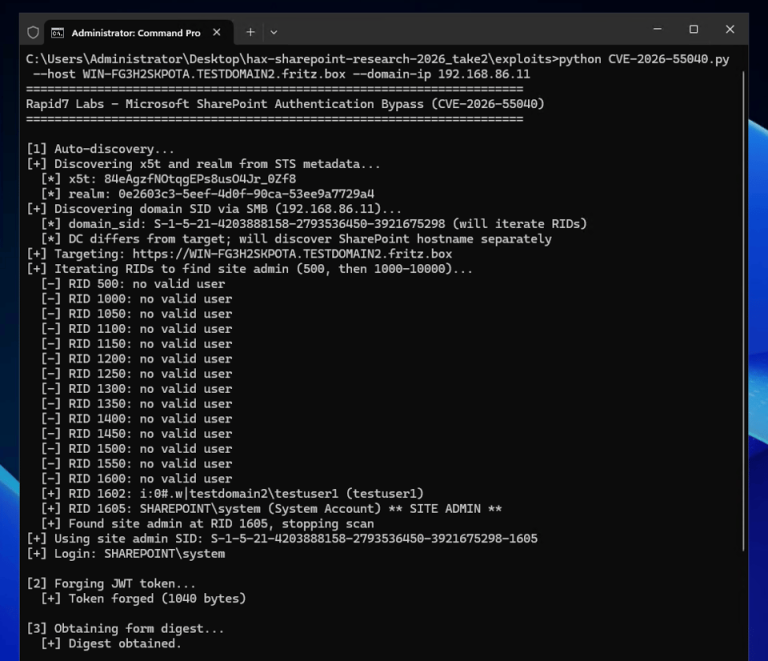
CVE-2026-55040 PoC Released for SharePoint Authentication Bypass CVE-2026-55040 SharePoint authentication bypass PoC forging a JWT token shown in a Rapid7 exploit terminal
  • Vulnerability Report

CVE-2026-55040 PoC Released for SharePoint Authentication Bypass

Do Son August 12, 2026 0
TL;DR Rapid7 has published a technical analysis and a working proof-of-concept for CVE-2026-55040. The flaw is a...
Read More Read more about CVE-2026-55040 PoC Released for SharePoint Authentication Bypass

Search

Translation

CVE ALERTS
πŸ“ˆ

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

πŸ›‘οΈ

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

πŸ™

GitHub Issues
Auto-create alert tickets without duplication.

πŸ“¬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

πŸ”€

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days β†’

🚨 Active Exploits in the Wild

  • CVE-2026-102255CVSS 10.0
    A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2026-105133CVSS 6.9
    A vulnerability was detected in Ahsay AhsayCBS up to 10.3.2. This affects the function checkSysPwd of the file...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2023-22894CVSS 4.9
    Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2016-3081CVSS 8.1
    Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled,...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-3306CVSS 10.0
    The mod_copy module in ProFTPD 1.3.5 allows remote attackers to read and write to arbitrary files via the...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-5477CVSS 7.5
    named in ISC BIND 9.x before 9.9.7-P2 and 9.10.x before 9.10.2-P3 allows remote attackers to cause a denial...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2021-3199CVSS 9.8
    Directory traversal with remote code execution can occur in /upload in ONLYOFFICE Document Server before 5.6.3, when JWT...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2026-94504CVSS 7.2
    Ninja Forms 3.15.3 stores an anonymous non-RTE textarea value and renders it without safe HTML encoding in the...
    Admin intel📅 Updated: Oct 7, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-93582CVSS 9.4
    The HTTP Basic Authentication modules in ((OTRS)) Community Edition 6 and prior accept the authenticated username from either...
    📅 Updated: Oct 12, 2026
  • CVE-2026-78357CVSS 9.1
    Previously issued authentication tokens are not immediately invalidated when an OTRS agent or customer user account is deactivated...
    📅 Updated: Oct 12, 2026
  • CVE-2026-108804CVSS 10.0
    A vulnerability was detected in TRENDnet TEW-751DR, TEW-752DRU and TEW733GR 1.03B01/1.03B03. Affected is the function fwrite of the...
    📅 Updated: Oct 12, 2026
  • CVE-2026-66086CVSS 9.8
    In the modem OTA stack, there is a possible stack-based buffer overflow due to improper validation of scheduling...
    📅 Updated: Oct 12, 2026
  • CVE-2025-58255CVSS 9.6
    Cross-Site Request Forgery (CSRF) vulnerability in yonisink Custom Post Type Images custom-post-types-image allows Code Injection.This issue affects Custom...
    📅 Updated: Oct 11, 2026
  • CVE-2025-59434CVSS 9.6
    Flowise is a drag & drop user interface to build a customized large language model flow. Prior to...
    📅 Updated: Oct 11, 2026
  • CVE-2025-9321CVSS 9.8
    The WPCasa plugin for WordPress is vulnerable to Code Injection in all versions up to, and including, 1.4.1....
    📅 Updated: Oct 11, 2026
  • CVE-2025-10147CVSS 9.8
    The Podlove Podcast Publisher plugin for WordPress is vulnerable to arbitrary file uploads due to missing file type...
    📅 Updated: Oct 11, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
Β© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.