 Do Son
Update Control Web Panel to version 1.29 now to patch CVE-2026-73695, CVE-2026-73696, and eight other flaws allowing unauthenticated root RCE.
CWP

Fenrisk releases full PoC exploit for CVE-2025-48703, a critical CWP RCE flaw. Learn how unauthenticated attackers hijack non-root users. Patch now!

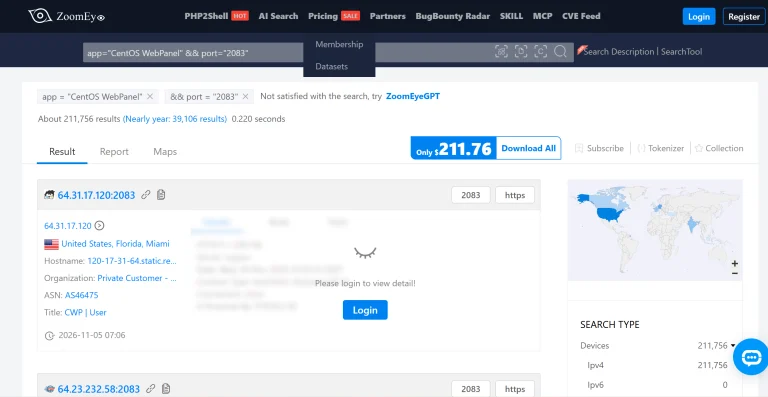
A critical flaw (CVE-2025-48703) in CentOS Web Panel allows unauthenticated RCE via authentication bypass and command injection, risking over 200,000 servers.