 Do Son
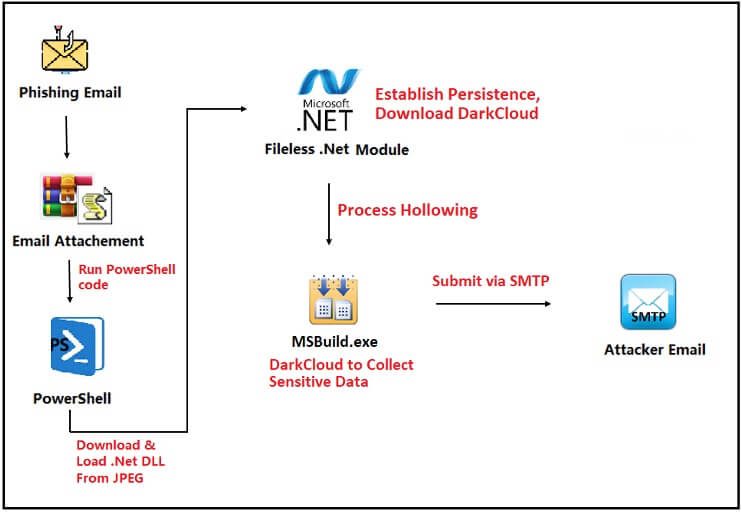
Fortinet uncovers a new DarkCloud stealer variant using a fileless, multi-stage attack chain with obfuscated PowerShell and process hollowing to evade detection and exfiltrate data.
DarkCloud

DarkCloud Stealer resurfaces in 2025 with AutoIt scripting and multi-stage obfuscation, targeting sensitive browser, email, and FTP credentials.