 Do Son
PostgreSQL security update 18.7 fixes 52 CVEs, including CVE-2026-6460 and 31 other code execution flaws. PostgreSQL 14 reaches end of life.
database security
Update MongoDB Server to 9.0.7 now to fix CVE-2026-118383, CVE-2026-120808, and 24 other flaws causing code execution, memory leaks, and crashes.
Discover seven unpatched phpMyAdmin vulnerabilities exposing servers to SQL injection and auth bypass. Learn how to secure your databases today.
The PostgreSQL project resolved 15 critical pgAdmin 4 vulnerabilities in version 9.19, fixing command injection flaw CVE-2026-116241 and credential leaks.
Six Apache CouchDB vulnerabilities, including CVSS 9.3 CVE-2026-86471, are fixed in 3.5.3. Retired Apache Cocoon gets four unpatched flaws.
MariaDB critical vulnerabilities, including CVE-2026-92262 (CVSS 9.9), risk remote code execution. Upgrade to the October 2026 releases.
The Redis RESTORE vulnerability CVE-2026-25243 is exploited in the wild, Defused honeypots show. Upgrade to Redis 8.6.3 or block RESTORE.
Progress fixed 31 MarkLogic Server vulnerabilities, including CVSS 9.9 privilege escalation flaws. Upgrade to MarkLogic 12.1 or 11.3.7 now.
Nine MariaDB vulnerabilities enable privilege escalation and code execution, rated up to CVSS 8.5. Upgrade to the fixed Server and Connector/C releases.
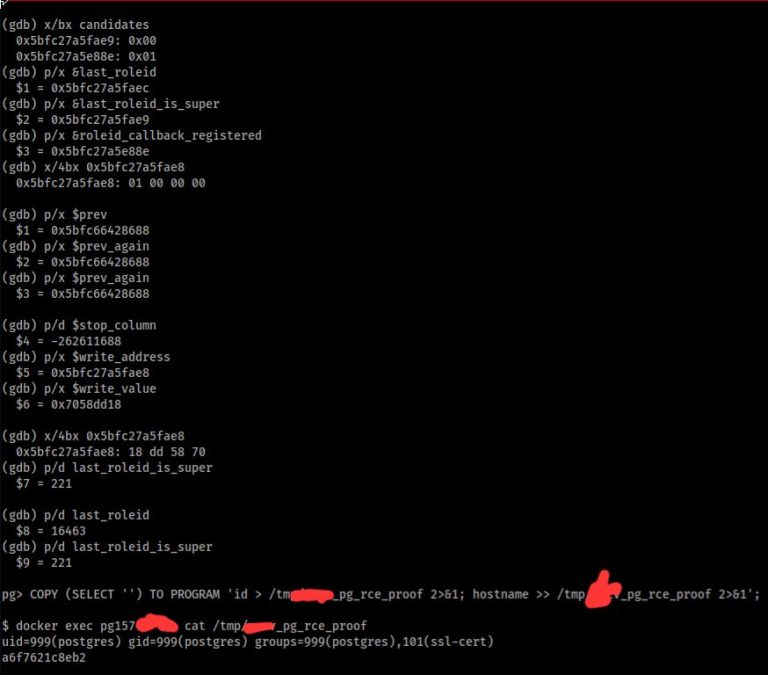
A critical PostgreSQL RCE vulnerability allows remote code execution. Details and PoC for this PostgreSQL RCE vulnerability are now public. Update now.
MongoDB patched critical MongoDB driver vulnerabilities across its ecosystem. Update your drivers to resolve these MongoDB driver vulnerabilities now.
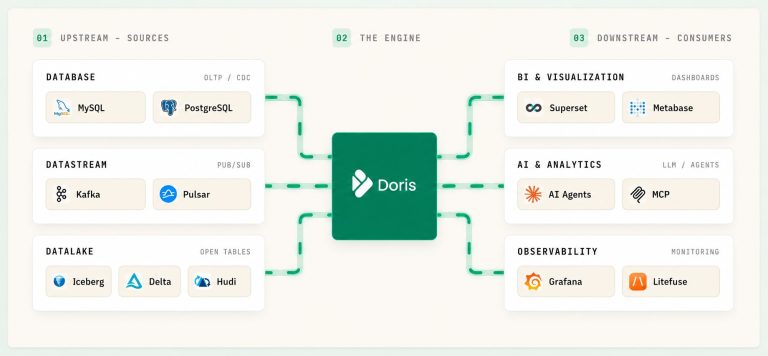
The team patched Apache Doris vulnerabilities in new updates. Learn how these Apache Doris vulnerabilities impact clusters and update now.
MongoDB fixed 24 MongoDB Server vulnerabilities, including a critical auth bypass (CVE-2026-82067) and unauthenticated denial of service flaws. Patch now.

PoC exploit code is public for a MariaDB remote code execution chain. A low-privilege account can run commands as mariadbd. Details inside.

CVE-2026-58048 lets cPanel users run SQL commands in root context, CVSS 9.4. A second flaw, CVE-2026-58047, enables request smuggling.
MongoDB patched 27 vulnerabilities across Server and Compass. The set includes memory corruption, RBAC bypass, and denial-of-service flaws. Update now.
Apache Doris vulnerability CVE-2026-58319 lets unauthenticated attackers hit FE HTTP admin APIs. Upgrade to Doris 3.1.0 now to close the flaw.

A critical IBM Db2 RCE flaw (CVE-2026-10109) allows pre-auth code execution. IBM patched it plus two other Db2 bugs. Update 11.5 and 12.1 now.

Three critical MariaDB server vulnerabilities, including a CVSS 10 flaw, allow attackers to execute shell commands. Patch your database servers immediately.
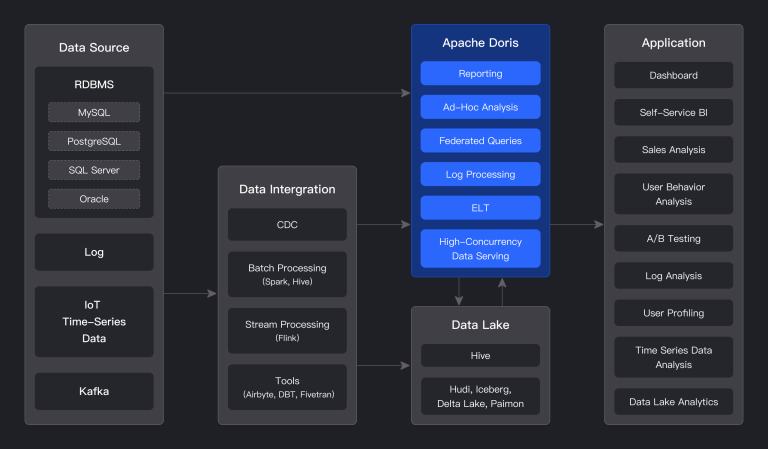
A critical Apache Doris SQL injection vulnerability identified as CVE-2025-66336 allows attackers to bypass authentication. Upgrade your servers now.

A critical MariaDB security flaw affects millions of servers. Learn about the 10.0 CVSS bug impacting recent community server releases.

A critical MCP Toolbox vulnerability exposes enterprise databases. Learn how this security flaw allows session hijacking and how to fix it.