 Do Son
A newly fixed Apache Ignite vulnerability allows arbitrary file read attacks via path traversal. Learn how to secure your database immediately.
database security
Stay secure with the latest Oracle security patch updates. Learn how these fixes address critical software vulnerabilities across multiple enterprise platforms.

PostgreSQL releases updates for versions 14-18 fixing 11 vulnerabilities (CVSS 8.8). Plus, critical End-of-Life deadline issued for Postgres 14.

Technical details and GitHub PoC exploits disclosed for PostgreSQL pgcrypto CVE-2026-2005. Low-privilege users can seize root superuser RCE. Patch now!

CVE-2026-8178 in Amazon Redshift JDBC Driver allows RCE via unsafe class loading. Protect your data warehouse and update to version 2.2.2 now!

pgAdmin 4 v9.15 fixes a 9.4 CVSS auth bypass and multiple RCE flaws. Attackers can execute OS commands via SQL tools. Upgrade your pgAdmin server now!

CVE-2026-44477 in CloudNativePG allows low-privilege users to gain root-level RCE via metrics exporters. Update to version 1.29.1 or 1.28.3 now!

Urgent: A memory corruption flaw in MongoDB time-series collections (CVE-2026-8053) enables server takeover. Patch to versions 8.3.2, 8.0.23, or 7.0.34 now.

ArcadeDB 26.4.1 fixes a critical 9.0 CVSS authorization bypass (CVE-2026-44221) that dismantles database isolation. Secure your multi-model data and patch now!
ElectricSQL reveals a critical 10.0 CVSS SQL injection (CVE-2026-40906). Attackers can hijack PostgreSQL and bypass tenant isolation. Patch to v1.5.0 now.
Critical 10.0 CVSS flaw in Firebird Database allows RCE via path traversal in the engine loader. Attackers gain root/SYSTEM privileges. Patch to 5.0.4+ now.

Dgraph (CVE-2026-40173) leaks admin tokens in plain text via unauthenticated debug endpoints. This critical 9.4 CVSS flaw allows full DB takeover. Patch now!
Dgraph patches a critical 10.0 CVSS flaw (CVE-2026-33976). Unauthenticated attackers can overwrite databases and read local files. Update to v25.3.1 now!

2M+ monthly users are at risk as MikroORM patches a critical 9.3 CVSS SQL injection flaw (CVE-2026-34220). Update to 6.6.10 or 7.0.6 immediately to stay safe.
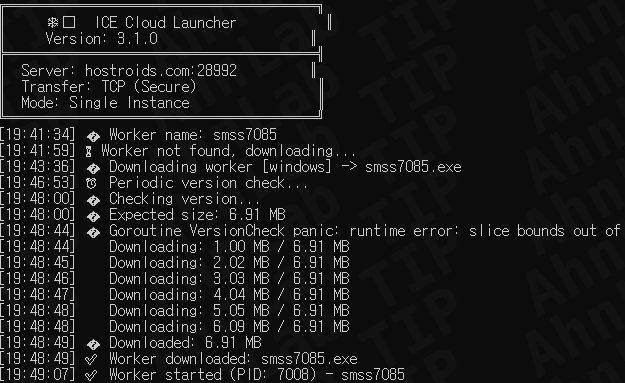
Larva-26002 strikes again with "ICE Cloud," a Go-based scanner using AI-assisted code to hijack MS-SQL servers. Discover the technical breakdown and defense.
MariaDB patches a high-severity buffer overflow (CVE-2026-32710) in its JSON validation function. Upgrade to 11.4.10 or 11.8.6 to prevent server crashes.

Bishop Fox publicly disclosed details of a critical 9.1 CVSS zero-click SQL injection in FortiClient EMS (CVE-2026-21643). Patch to 7.4.5 immediately.

A critical SQL injection flaw (CVE-2026-2413) in the Ally WordPress plugin exposes 400K+ sites to database theft. Update to version 4.1.0 immediately.

Vitess patches critical flaws (CVE-2026-27969 & 27965) where poisoned backup manifests lead to path traversal and RCE during restoration. Update to v23.0.3 now.

Critical SQL injection flaw (CVE-2026-26198) in ormar Python ORM allows unauthenticated attackers to leak entire databases. Update to version 0.23.0 immediately!

Urgent: PostgreSQL patches 5 flaws, including 3 critical RCEs (CVSS 8.8). Attackers can execute code as OS user via text manipulation. Update v14-18.
MongoDB patches high-severity flaw CVE-2026-25611. Unauthenticated attackers can crash servers via memory exhaustion. Update to v8.2.4 or v8.0.18 now.