
 Do Son
Trellix details a DCRat campaign using SVG HTML smuggling and process hollowing to deploy DarkCrystal RAT via a Colombian judicial lure.
DCRat

PHALT#BLYX is a malware campaign using fake Booking.com alerts and BSOD screens to trick hotel staff into installing Russian-linked RATs.

A notorious cyber-espionage group known for terrorizing South American institutions has launched a new campaign against the...

Fortinet exposes a DCRat campaign impersonating a Colombian government agency, using obfuscated multi-stage infection, steganography, and AMSI bypass to deliver the RAT.

Censys uncovers "sostener.vbs," an obfuscated VBScript launching a multi-stage RAT delivery pipeline, affecting dozens and potentially linked to Blind Eagle APT.

IBM X-Force warns of a new phishing campaign by Hive0131 targeting Colombian users with DCRat malware via fake legal notices.

Uncover the ongoing steganographic campaign that distributes malware like Remcos RAT. Learn how it operates.

Stay informed about the DarkCrystal RAT threat targeting Ukraine's defense sector and learn how to protect yourself from cyberattacks.
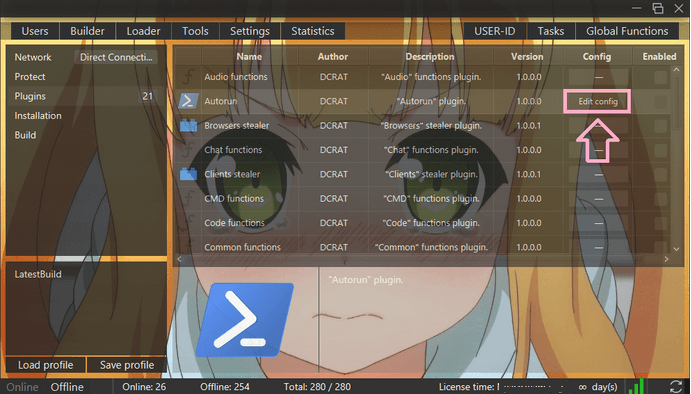
Explore the DCRat backdoor issue and how it utilizes Malware-as-a-Service to infect users through deceptive YouTube videos.

Protect your organization from PythonRatLoader: a sophisticated malware loader that distributes harmful remote access trojans (RATs).

Learn about the first observed use of HTML smuggling by DCRat, a powerful remote access trojan. Find out how this technique allows cybercriminals to deploy malware undetected.