 Do Son
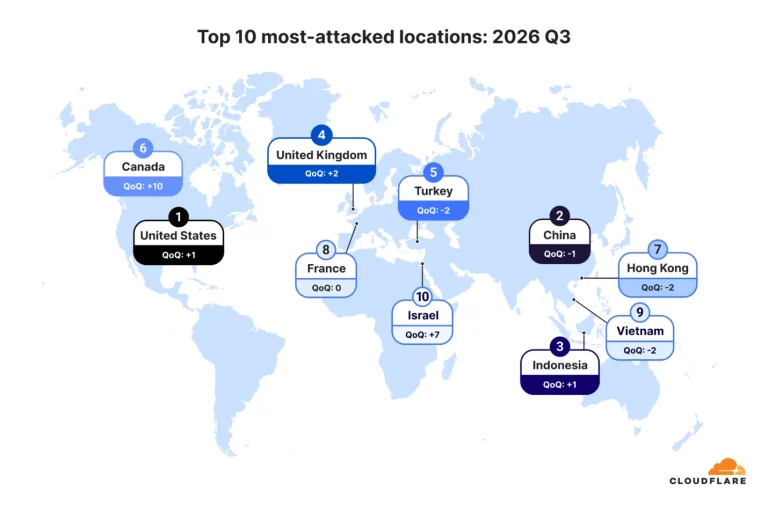
The Cloudflare DDoS report Q3 2026 reveals 18.2M network attacks, a 208% surge in short-burst floods, and a major shift toward DNS and UDP attacks.
DDoS attacks

Read the latest Gafgyt malware analysis revealing how the dangerous COXMO botnet variant spreads via standalone scripts.

The US DOJ, alongside Canada and Germany, has dismantled four massive IoT botnets responsible for record-breaking 30 Tbps DDoS attacks worldwide.

NCSC warns of Russian group NoName057(16) targeting UK sectors with DDoS attacks. Defenders must ensure scalability and plan for graceful degradation.

Cloudflare’s 2025 report reveals a 19% traffic spike, Googlebot’s dominance in the "AI bot war," and the rise of post-quantum encryption for 52% of users.

Explore the rise of INDOHAXSEC, a new hacktivist group in Indonesia making headlines with cyberattacks and DDoS activities.
Discover how a newly discovered IoT botnet is targeting organizations globally with large-scale DDoS attacks.

Discover cShell, a new strain of DDoS malware targeting poorly managed Linux SSH servers. Learn how it exploits weak credentials to turn servers into DDoS bots.

Discover the world of hacktivist groups and their impact on geopolitics. Explore the tactics, players, and implications of state-linked hacktivism.

Discover the scale and sophistication of the NSOCKS botnet: a criminal proxy network aiding in DDoS attacks, phishing, and malware obfuscation.

Discover the details about LameDuck, a pro-Islamic, anti-Western group responsible for over 35,000 DDoS attacks worldwide.

Uncover the latest cyber threats targeting the European Union. From DDoS attacks to ransomware, gain insights into the challenges faced by the EU.

The authorities' actions were carried out as part of Operation PowerOff, aimed at curbing the activities of DDoS-for-hire service

Resurgence of Mirai botnet variants, coupled with AI-enhanced DDoS attacks, underscores the critical need for robust cybersecurity measures

Chalubo malware was highly active in late 2023 and early 2024, with over 330,000 unique IP addresses communicating with known C2 servers

Goldoon botnet is ruthlessly exploiting a CVE-2015-2051 vulnerability in D-Link devices to commandeer them for malicious activities

Lucifer DDoS botnet is exploiting misconfigurations and vulnerabilities in Apache Hadoop and Apache Druid (CVE-2021-25646)

According to Qrator Labs, 2023 was a year of marked transformation in the world of Distributed Denial of Service (DDoS) attacks.

one of the internet giants, Namecheap has been hit by a series of DDoS attacks that threaten to disrupt its operations.

As investigators delve deeper into the labyrinthine world of the UAC-0027 hacking group, they have uncovered 486 IP addresses

Dubbed 'Operation Japan,' this campaign unfolds against the backdrop of Japan's controversial decision to release treated water

These instances are being exploited by hacker to transform machines into botnets for DDoS attacks, primarily aiming to expand a botnet known as OracleIV