Skip to content
October 13, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Malware
  • Cloudflare successfully blocked DDoS attacks up to 2 Tbps
  • Cyber Security
  • Malware

Cloudflare successfully blocked DDoS attacks up to 2 Tbps

Do Son November 16, 2021 3 minutes read
Cloudflare DDoS attacks 2 Tbps
Add Daily CyberSecurity as a preferred source on Google

In October 2016, a hacker used the Mirai Internet of Things worm to control millions of Internet of Things devices to launch an attack on the US DNS service provider DYN. After the attack, many well-known websites on the east coast of the United States could not be accessed.

In the next few years, Mirai appeared in countless variants. The core functions of these variants are to infect IoT devices with built-in password combinations. The most common one is the camera IP. Some camera IPs use the default account password and have never been modified, so it is easy to be infected.

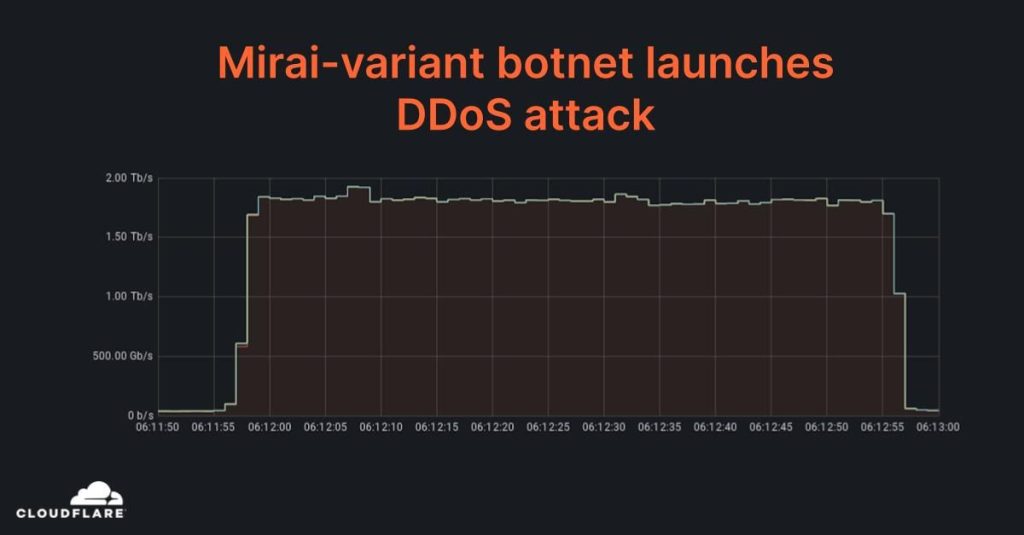
Recently, Cloudflare released a blog post introducing the company’s latest intercepted DDoS attack. The instantaneous traffic of this attack was close to 2 Tbps and was initiated by approximately 15,000 bots. These robots are located in IoT devices and GitLab instances without patches, and Mirai is still behind the robots.

Earlier, a security company discovered a vulnerability in GitLab, and the CVSS score of this vulnerability was as high as 10 points/out of 10 points. If you successfully exploit the vulnerability, an attacker can directly invade the server where the GitLab instance is located and run arbitrary code, for example, to run worms such as Mirai. Since the details of the vulnerabilities have been made public, more and more hackers will exploit these vulnerabilities. Scanning shows that half of the 60,000 GitLab instances exposed on the public network have not been patched.

The attack intercepted by Cloudflare has many infected GitLab instances. Mirai variants infected these instances and formed a botnet to launch the attack. It is difficult for 15,000 robots to directly launch an attack of up to 2 Tbps. Cloudflare analyzes that this is a multi-carrier attack. The robots may combine DNS amplification attacks and use UDP floods, etc.

Cloudflare has observed a significant increase in DDoS attacks at the network layer in the third quarter. Although the fourth quarter is not over yet, CloudFlare has now noticed that the number of large-scale DDoS is increasing.

“Another key finding from our Q3 DDoS Trends report was that network-layer DDoS attacks actually increased by 44% quarter-over-quarter,” said Omer Yoachimik, product manager at Cloudflare. “While the fourth quarter is not over yet, we have, again, seen multiple terabit-strong attacks that targeted Cloudflare customers.”

Rapid7 has urged GitLab users to update the latest version of GitLab as soon as possible. “In addition, ideally, GitLab should not be an internet-facing service. If you need to access your GitLab from the internet, consider placing it behind a VPN.”

Related coverage

  • Report: China is on top 1 on Distribution of DDoS attacks
  • Trojanized VPN Installer Deploys NKNShell Backdoor, Using P2P Blockchain and MQTT Protocols for Covert C2
  • LUMMA Malware: Cybercriminals Elevate Tactics with Fake Invoice Campaign
  • US Denounces Russian Cyberattacks Targeting Germany, EU Nations
  • StrelaStealer Malware Intensifies Attacks on European Email Users, Avoiding Russia
  • Urgent Alert: “Free Wedding Invite” Scam Targets Senior Citizens, Steals Sensitive Data
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: cloudflare DDoS attacks

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-104935CVSS 8.6
    Authentication bypass by spoofing in ICS before version 25.1.3.0 allows a remote unauthenticated attacker to execute arbitrary commands....
    Admin intel📅 Updated: Oct 13, 2026
  • CVE-2026-102255CVSS 10.0
    A Pre-authentication SSRF vulnerability exists in the SMA1000 Appliance Work Place interface due to an unintended alternate access...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2026-105133CVSS 6.9
    A vulnerability was detected in Ahsay AhsayCBS up to 10.3.2. This affects the function checkSysPwd of the file...
    Admin intel📅 Updated: Oct 9, 2026
  • CVE-2023-22894CVSS 4.9
    Strapi through 4.5.5 allows attackers (with access to the admin panel) to discover sensitive user details by exploiting...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2016-3081CVSS 8.1
    Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled,...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-3306CVSS 10.0
    The mod_copy module in ProFTPD 1.3.5 allows remote attackers to read and write to arbitrary files via the...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2015-5477CVSS 7.5
    named in ISC BIND 9.x before 9.9.7-P2 and 9.10.x before 9.10.2-P3 allows remote attackers to cause a denial...
    CISA KEV📅 Added to KEV: Oct 8, 2026
  • CVE-2021-3199CVSS 9.8
    Directory traversal with remote code execution can occur in /upload in ONLYOFFICE Document Server before 5.6.3, when JWT...
    CISA KEV📅 Added to KEV: Oct 8, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-109705CVSS 9.6
    Sandbox escape, site isolation issue due to incorrect boundary conditions, use-after-free in the Networking component. This vulnerability was...
    📅 Updated: Oct 13, 2026
  • CVE-2026-109707CVSS 9.6
    Sandbox escape due to use-after-free in the Networking component. This vulnerability was fixed in Firefox 158 and Firefox...
    📅 Updated: Oct 13, 2026
  • CVE-2026-77366CVSS 9.9
    obsidian-tc is a governed, agent-ready Model Context Protocol server for Obsidian vaults. Prior to 1.3.1, tool dispatch does...
    📅 Updated: Oct 13, 2026
  • CVE-2026-55695CVSS 9.1
    FearlessCMS is a flat-file content management system centered on simplicity and open source. In 0.1.2b and earlier, an...
    📅 Updated: Oct 13, 2026
  • CVE-2026-55675CVSS 10.0
    The Salty documentation repository builds and deploys the docs.saltbox.dev website. Prior to commit 649c9aea2daef1168eeb0415b44e65dbbde9f220, .github/workflows/trigger-pr-build.yml records an untrusted...
    📅 Updated: Oct 13, 2026
  • CVE-2026-96012CVSS 9.9
    IBM Db2 Mirror for i 7.4, 7.5, and 7.6 is vulnerable to privilege escalation. An authenticated attacker could craft...
    📅 Updated: Oct 13, 2026
  • CVE-2026-90920CVSS 9.8
    IBM Maximo AI Service 9.1.0, and 9.2.0 could allow a remote attacker to execute arbitrary code due to...
    📅 Updated: Oct 13, 2026
  • CVE-2026-82101CVSS 9.6
    IBM DataStage on Cloud Pak for Data 5.4.0.0 could allow a remote authenticated attacker to cause a denial...
    📅 Updated: Oct 13, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.