
 Do Son
The Dysphoria botnet uses blockchain ENS/SNS domains for covert C2 and turns victims into relays. XLab tracked over 200,000 bots in this IoT DDoS botnet.
DDoS-for-hire
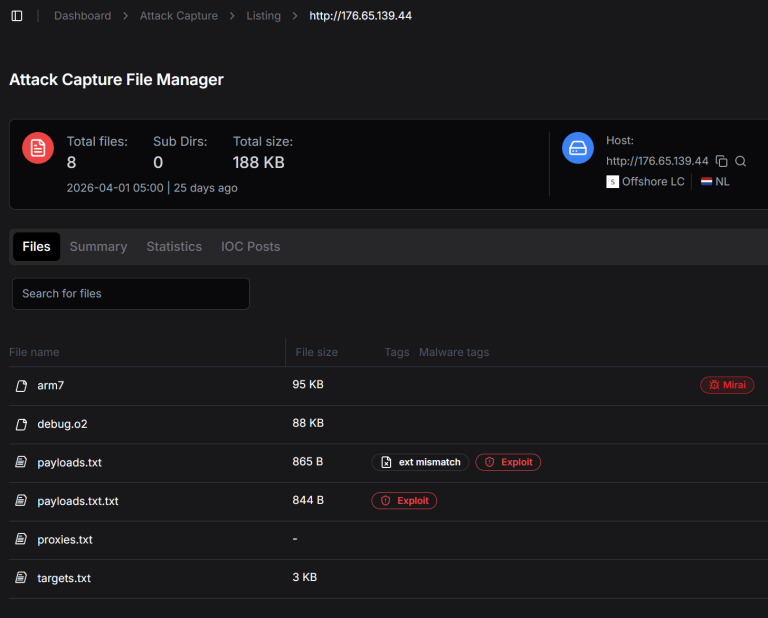
Hunt Intelligence dismantles xlabs_v1, a Mirai-derived botnet targeting 4M Android devices via port 5555. See how an exposed server leaked the entire toolkit.
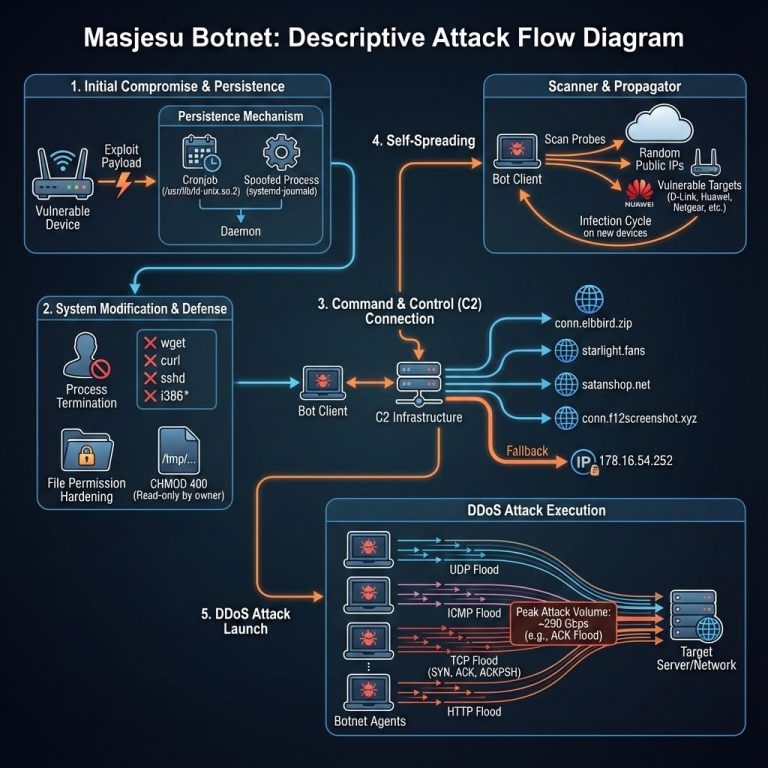
Trellix ARC reveals Masjesu, a stealthy, professional IoT botnet operational since 2023. Targeted DDoS-for-hire with a low-profile strategy. Patch now!