
 Do Son
The vulnerability, CVE-2024-35205, arises from the application's failure to properly sanitize filenames before processing them
Dirty Stream
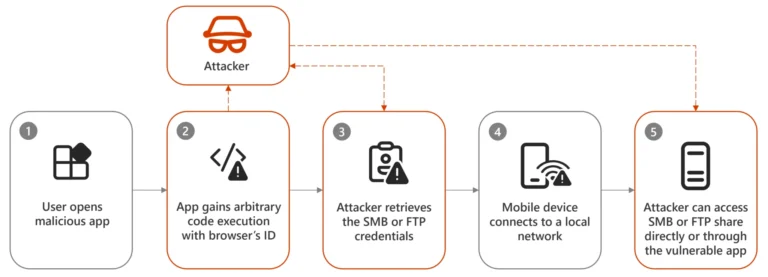
Dirty Stream exploits path traversal vulnerabilities when applications share data using Android's ContentProvider components