 Do Son
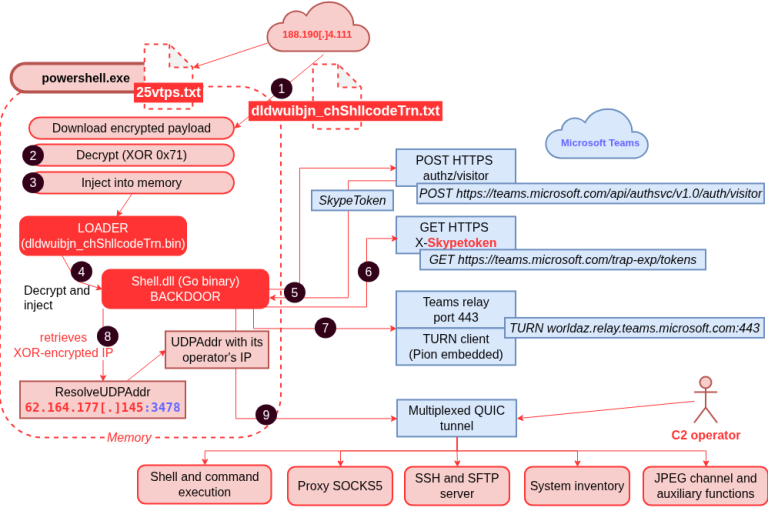
A new DragonForce backdoor hides in Microsoft Teams TURN relays and falls back to MQTT. See how it works and how defenders can spot it.
DragonForce
DragonForce ransomware deployed Backdoor.Turn, a Microsoft Teams backdoor that hides C2 in Teams TURN relays. Symantec details the novel technique.

S2W reveals DragonForce is a "cartel" hacking rivals like BlackLock. Built on LockBit 3.0 code, they offer "Ransombay" services. A decryptor was found.

Yarix exposes the new Qilin-LockBit-DragonForce cartel. Is it a powerful merger or a desperate PR stunt for a "dead" LockBit? Find out.

Acronis exposed DragonForce's evolution: the ransomware is compiled with MinGW, uses BYOVD drivers to terminate EDR, and contains fixes to prevent decryption of its Conti V3 derived codebase.

Medusa & DragonForce RaaS groups weaponize SimpleHelp RMM flaws (CVE-2024-57726/7/8) to gain SYSTEM-level access to customer networks. Immediate patch needed.

Darktrace exposed a DragonForce RaaS attack on a manufacturer. The multi-phase intrusion used brute force and OpenVAS for recon, then exfiltrated data over SSH to a Russian-based malicious host.

A joint advisory from US, UK, Canada, and Australia warns of Scattered Spider's evolving tactics, now using DragonForce ransomware, spearphishing, SIM swapping, and MFA fatigue to compromise systems.

Qilin ransomware is rapidly dominating the RaaS landscape, as rivals like RansomHub and LockBit face collapse, internal chaos, and public defacements by "XOXO from Prague."

Attackers compromised an MSP's RMM tool (SimpleHelp) to deploy DragonForce ransomware across customer environments.

UNC3944 resurfaces as Scattered Spider, linked to DragonForce and RansomHub in new retail attacks. Mandiant warns of social engineering escalation.
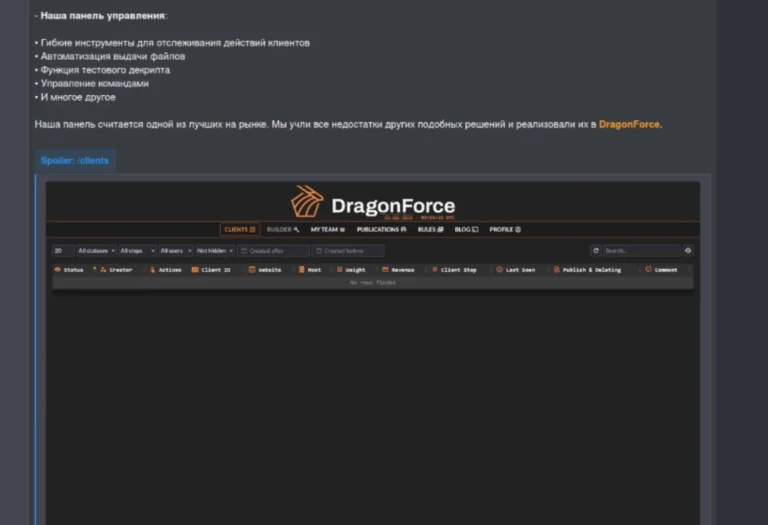
DragonForce ransomware cartel targets UK retailers with Conti-based payloads, RansomBay leaks, and phishing attacks, warns SentinelOne report.