 Do Son
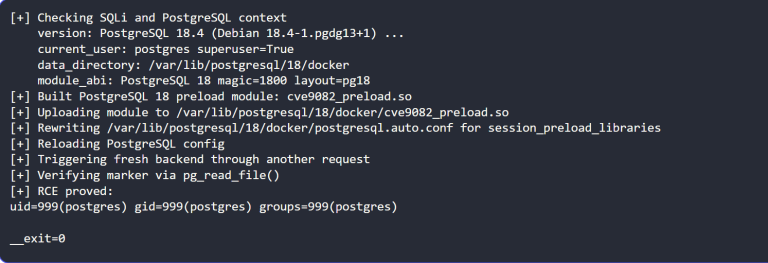
A critical Drupal SQL injection exploit is active in the wild. Read the analysis of this flaw now that the wild exploit PoC is fully public.
Drupal Core

Urgent: Drupal releases patches for highly critical SQLi flaw CVE-2026-9082. Unauthenticated attackers can exploit PostgreSQL backends for full remote RCE.