 Do Son
eSentire ties the Cruciferra malware loader to ClickFix EDR killer attacks that abuse a signed driver to stop 145 security processes.
EDR Killer
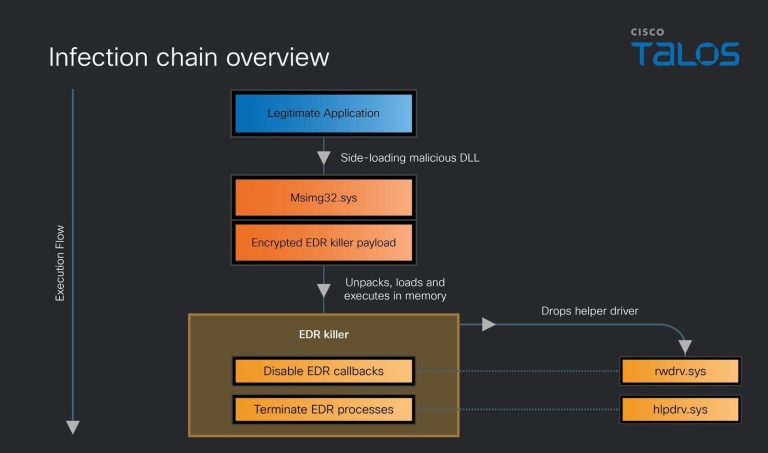
Cisco Talos unmasks a Qilin ransomware payload that terminates 300+ EDR drivers and manipulates the Windows kernel. See how this "EDR Killer" stays invisible.

Aryaka Threat Labs exposes BlackSanta, a Russian-linked malware targeting HR teams with fake resumes to deploy an EDR-killer and steal crypto wallets.

GOLD BLADE (RedCurl) targets Canadian firms (80% of attacks) with espionage and QWCrypt ransomware. The group uses fake resumes and a BYOVD EDR killer (Zemana driver) to disable security controls.

Makop ransomware operators now use GuLoader and BYOVD (ThrottleStop.sys) to bypass EDR and security. The "low-effort" campaign targets RDP-exposed networks, with 55% of attacks aimed at India.

DeadLock Ransomware uses BYOVD (Baidu driver exploit) and the EDRGay.exe loader to kill EDR/AV at the kernel level. It uses a custom stream cipher and deletes shadow copies to prevent recovery.

The Shanya Crypter (VX Crypt) is a new PaaS used by Akira/Medusa to bypass EDR. It deploys a kernel driver attack to kill security products and uses PEB manipulation for stealth.

WithSecure exposed TangleCrypt, a new ransomware packer that uses LZ78/XOR and embedded PE resources to hide the STONESTOP EDR killer. However, coding flaws cause unexpected crashes.

Explore the threat of Poortry: a malicious toolset designed to undermine endpoint detection and response (EDR) software on Windows systems. Learn how it bypasses security measures and adapts to evade detection.